Malaysia’s industrial sectors face rising OT and ICS cyber threats. Learn how to secure operational technology, meet NACSA requirements, and protect critical infrastructure.
Malaysia’s industrial sectors face rising OT and ICS cyber threats. Learn how to secure operational technology, meet NACSA requirements, and protect critical infrastructure.
Learn how SIEM works, why BNM RMiT mandates centralised logging, and how Simply Data SOC uses SIEM to detect threats for Malaysian enterprises. Read now.
Discover how agentic AI is transforming SOC operations in Malaysia — automating L1/L2 triage, cutting false positives, and accelerating MTTD/MTTR. Read the full guide.

Discover how threat intelligence strengthens Malaysian SOC teams — from IOC feeds and MITRE ATT&CK mapping to reducing dwell time. Built for Malaysian IT leaders.
BNM Risk Management in Technology policy guide: control domains, SOC monitoring expectations, third-party risk, and incident reporting. Checklist for Malaysian banks.
Managed SOC vs in-house SOC in Malaysia: compare operating models, 24/7 coverage, AI detection and RMiT compliance to make the right choice.
Learn how digital forensics incident response (DFIR) works in Malaysia — NACSA 72-hour reporting, chain of custody, DFIR lifecycle, and what to look for in a DFIR provider.
Discover how dark web monitoring helps Malaysian businesses detect leaked credentials, PII, and card data early — before attackers exploit them. Learn more.
In today’s interconnected world, businesses are under constant threat from cybercriminals looking to exploit vulnerabilities in digital infrastructure. To stay ahead, organizations must invest in real-time security intelligence, a critical aspect of a Security Operations Center (SOC). Simply Data Threat Intelligence Database, specifically built for Malaysia, offers actionable insights to help businesses detect, prevent, and […]
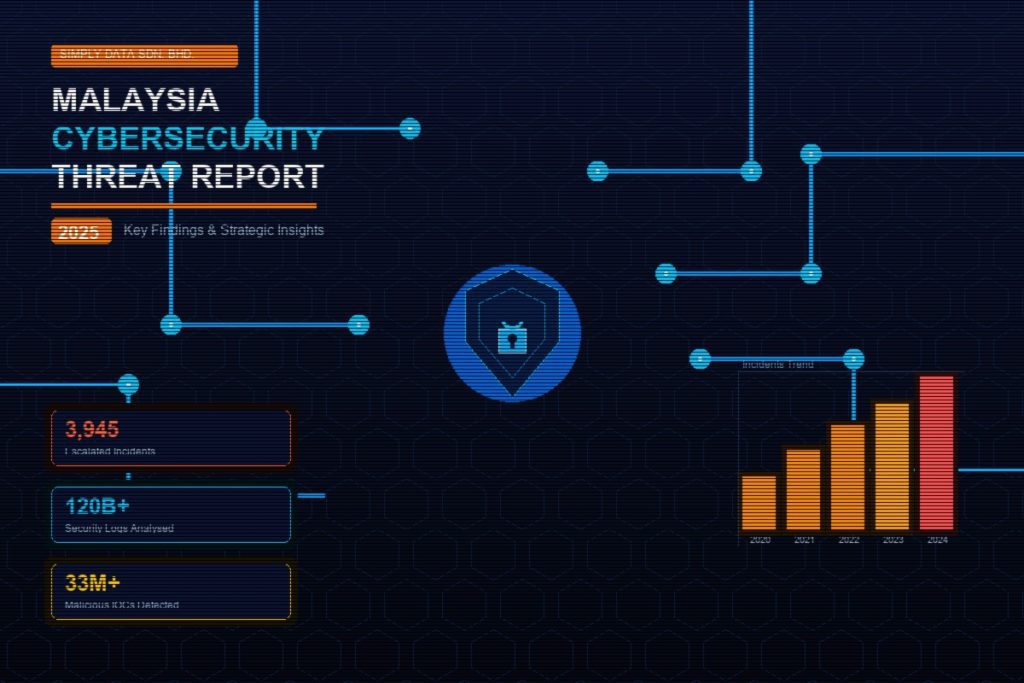
Simply Data 2025 Malaysia Cybersecurity Threat Report analyses 120B+ security logs, 3,945 escalated incidents, and 33M+ malicious IOCs. Discover the top threats targeting Malaysian organisations and what to do now.