24/7 SOC Monitoring for Banks in Malaysia: What RMiT Expects and What to Ask a Provider
24/7 SOC monitoring for banks is continuous security monitoring of critical systems and supporting infrastructure. For Malaysian financial institutions covered by RMiT, the September 2026 policy addresses proactive SOC monitoring and disaster recovery. Simply Data provides a 24×7 Security Operations Centre service; banks should assess its scope against their requirements.
What does RMiT say about SOC monitoring for financial institutions?
RMiT S 11.9 requires continuous, proactive monitoring through a SOC, while Appendix 5 Part C describes 24×7 operation with disaster recovery arrangements. The current document was issued on 25 September 2026. Use these provisions to frame the assessment of monitoring coverage, operational resilience and supporting evidence.
For procurement, translate that expectation into questions about the actual service. Which critical systems are covered? Which supporting infrastructure feeds the SOC? Who investigates an alert overnight? How does monitoring continue if the primary operating environment becomes unavailable? Ask the provider to demonstrate these arrangements through documented procedures and an agreed exercise.
A proposal for 24/7 SOC monitoring for banks should explain how monitoring connects to the institution’s incident management process. Define who assesses business impact, who authorises containment and who communicates with management. A dashboard alone does not establish those responsibilities; put the operating arrangements into the service scope and escalation procedures.
Build a requirements matrix linking each applicable provision to a control owner, service deliverable and evidence item. The Simply Data guide to BNM RMiT compliance in Malaysia can support that discussion. Keep the official policy document alongside the matrix so reviewers can distinguish regulatory requirements from proposed implementation choices.
What should 24/7 SOC monitoring for banks cover in practice?
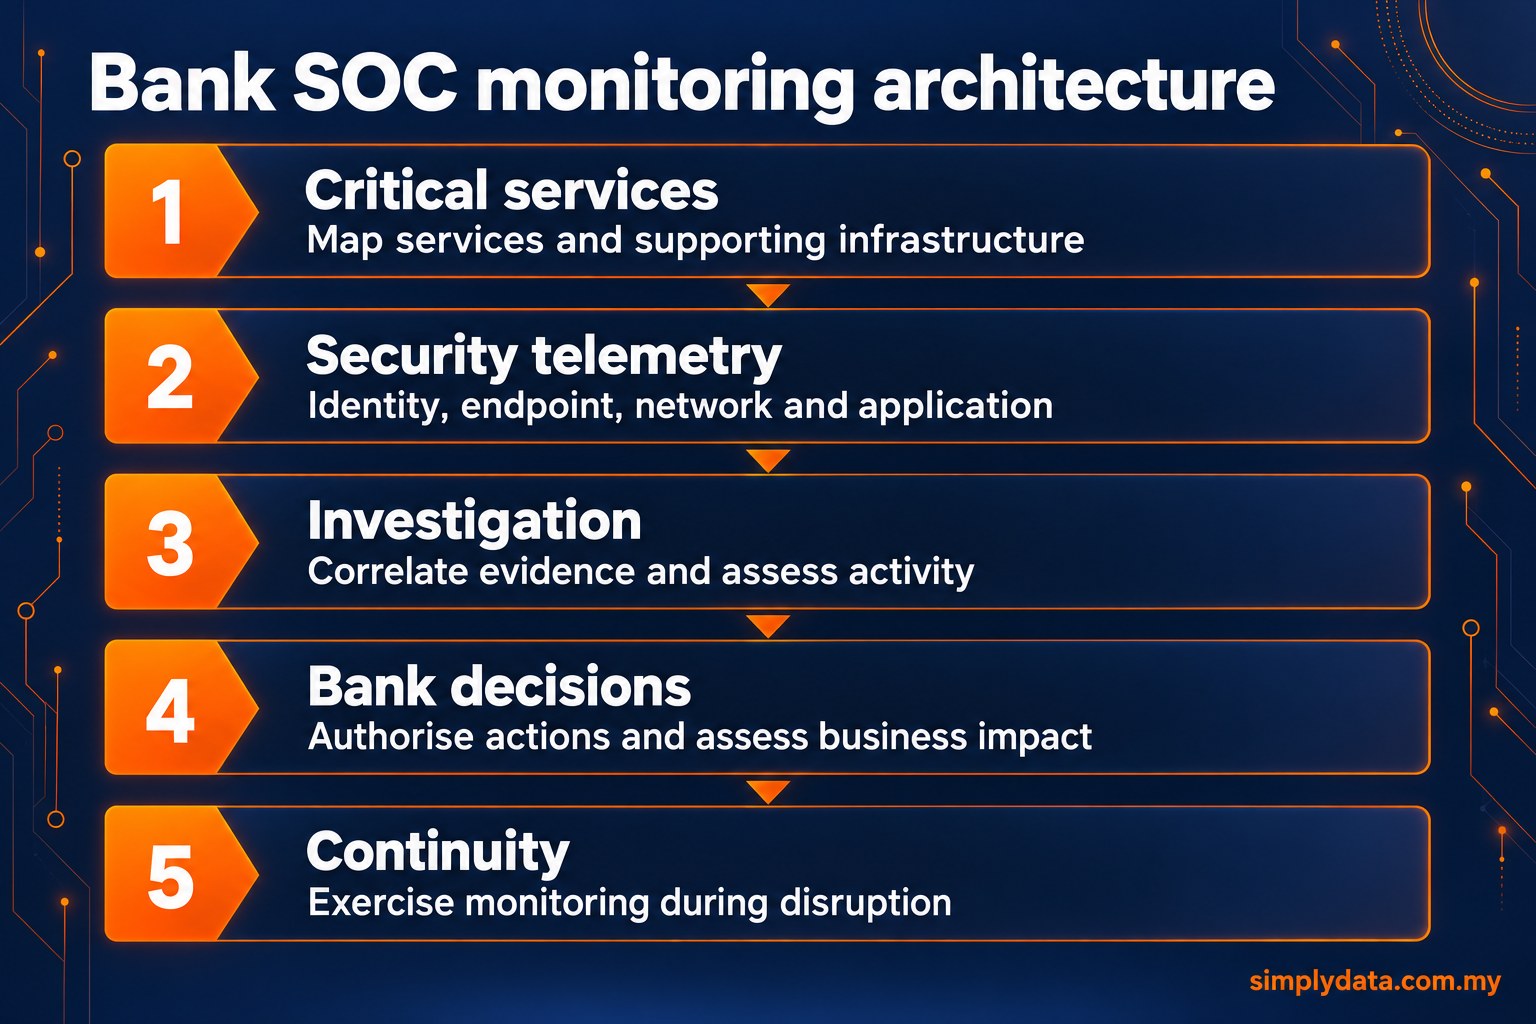
Define 24/7 SOC monitoring for banks across people, technology and decisions. Ask how analysts receive work between shifts, how unresolved investigations remain visible and how an escalation reaches the bank’s authorised decision-maker. Include weekends, public holidays and periods when the usual application owner is unavailable. Exercise the contact arrangements before relying on them during an incident.
Specify how the provider identifies gaps in monitoring. Request examples of how missing log feeds, failed integrations and changes to collection settings are recorded and escalated. Establish who restores each feed and how the bank receives confirmation that monitoring has resumed. Treat visibility into collection failures as an explicit acceptance criterion.
Ask for a walkthrough of a shift handover using a fictional investigation. The handover should let the receiving analyst understand the evidence, outstanding questions, actions already authorised and next decision required. Repeat the walkthrough with the primary monitoring environment unavailable to examine the proposed continuity arrangements.
Agree service measures that help the bank judge investigation quality. Request reporting on coverage gaps, unresolved cases, detection changes and completed improvement actions. Define how each measure is calculated and reviewed. When comparing providers, use the same evidence requests across proposals so differences in scope remain visible.
Which data sources should a bank SOC monitor first?
For 24/7 SOC monitoring for banks, start with a map of critical services and their dependencies. Identify the identities, endpoints, applications, network controls and administrative systems that support each service. Then agree detection scenarios and the evidence needed to investigate them. This makes onboarding a discussion about security visibility rather than simply the number of connected devices.
Prioritise identity and privileged access alongside externally accessible services. Ask how an analyst would investigate an unusual administrator login, a privilege change or suspicious remote access. For each scenario, request a demonstration of the available evidence and the information the bank must supply, such as an approved maintenance record or accountable system owner.
Next, examine endpoint, network, application and cloud visibility against the agreed scenarios. Include relevant SaaS administration and security events where those services support the institution’s operations. Record exclusions explicitly. If an application cannot provide the required event, assign an owner to resolve the gap or document an alternative source of evidence.
RMiT S 10.42 requires relevant network device logs to be retained for investigation and forensic purposes for at least three years. Ask how retention, retrieval, access control and export will work. Distinguish the period available for routine searching from the arrangements for retrieving archived evidence.
Before accepting a monitoring service, run an investigation exercise across the proposed sources. Ask an analyst to connect a fictional privileged login with endpoint and network activity. Record missing context, timestamp inconsistencies and retrieval difficulties, then assign corrective actions before expanding the monitoring scope.
In-house, hybrid or managed: which SOC model fits a Malaysian bank?
Choose a model for 24/7 SOC monitoring for banks by examining which operational responsibilities the institution can sustain and which it wants a provider to perform. Compare analyst coverage, detection engineering, platform administration, investigation support and continuity arrangements. Keep decision authority explicit in every model, especially where an action could affect a critical service.
| SOC model | Operating arrangement | Evidence to request |
|---|---|---|
| In-house | Bank operates the monitoring team and platform. | Staffing, handovers, detection maintenance and continuity exercises. |
| Hybrid | Bank and provider divide defined monitoring responsibilities. | Shared case ownership, access boundaries and escalation exercises. |
| Managed | Provider performs the contracted monitoring activities. | Service scope, investigation records, assurance and exit arrangements. |
For a hybrid arrangement, write down where responsibility changes hands. Specify who tunes a detection, who requests additional evidence and who closes an investigation. Use a shared scenario to test those boundaries. An escalation should identify the decision needed and the person authorised to make it.
For managed coverage, agree access to case records and the process for returning or exporting evidence when the arrangement ends. Review subcontracting, administrative access and service changes during due diligence. The managed SOC versus in-house SOC comparison provides a starting point for discussing the operating model.
What should a bank ask a managed SOC provider before signing?
Begin with licensing. Managed SOC monitoring and penetration testing are licensable services under the Cyber Security Act 2024, Act 854. Request the licence relevant to the proposed service and verify the contracting entity. Treat service licensing and assurance documentation as separate parts of the assessment.
Ask for a sample investigation record with sensitive information removed. Assess whether it explains the trigger, evidence reviewed, investigative reasoning, unresolved questions and requested action. Then ask the provider to explain how it reviews analyst work and updates detections when an investigation reveals a gap.
When assessing 24/7 SOC monitoring for banks, examine automation boundaries directly. Which activities are automated? Which findings receive analyst review? How are errors investigated and changes approved? Agree the authority required for any proposed response action, and document how the bank can inspect the evidence supporting an escalation.
Ask how monitoring is tested against independent security assessments. RMiT Appendix 5 Part D specifies quarterly vulnerability assessments and annual intelligence-led penetration testing; S 11.6 specifies red-team simulation at least every three years. Check the official provisions when defining the applicable scope.
Request an example of how assessment findings become detection improvements, with an owner and a retest plan. Use the 2026 managed SOC guide for Malaysia to structure broader procurement questions. Evaluate managed detection and response services against the investigation and response support the institution wants included.
What should a bank SOC do when a DDoS attack may be a decoy?
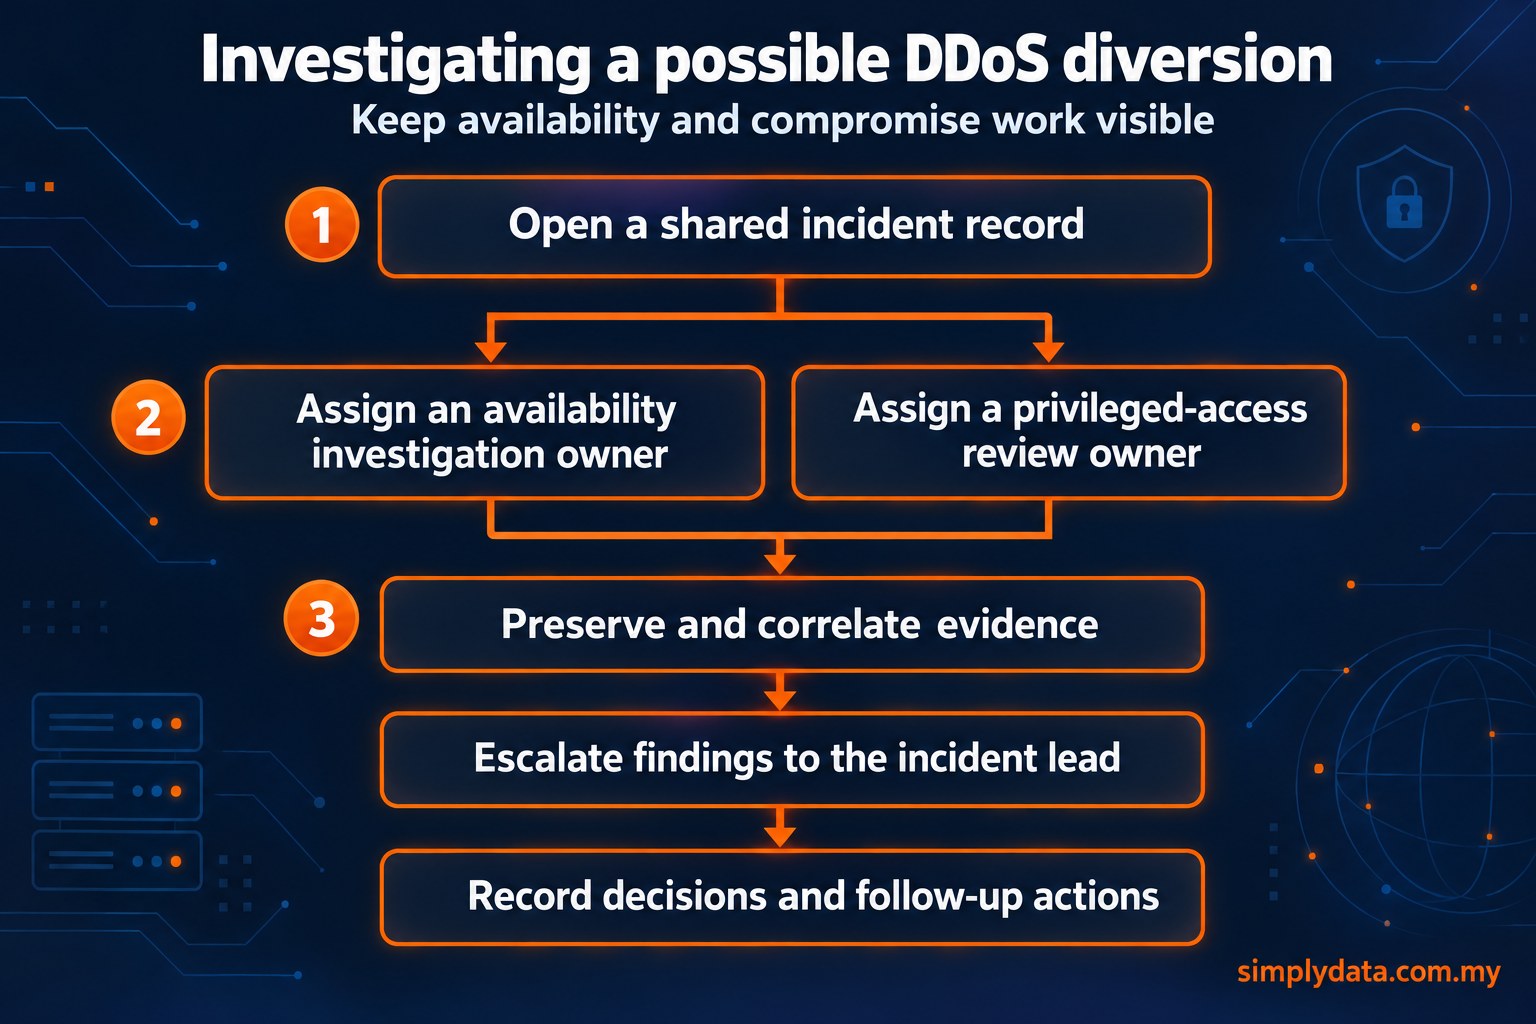
Maintain a parallel investigation into identity and privileged activity while the availability issue is addressed. NC4 advisory NC4-ALR-2026-000008 warns Malaysian financial institutions that DDoS activity may provide cover for an intrusion and highlights privileged identity protection. Use that scenario to test coordination between security and network teams.
Assign separate owners to service availability and suspected compromise, with a shared incident lead. Review administrator activity, remote access, privilege changes and unexpected configuration changes during the disruption. Preserve relevant evidence and record investigative decisions. Give the identity investigation a defined owner so attention to restoring service does not displace it.
Use a tabletop exercise to rehearse competing demands: restoring access, investigating suspicious activity and briefing decision-makers. Agree who evaluates regulatory reporting obligations under each applicable regime. Keep PDPA, NACSA and BNM assessment paths separate in the playbook, with the bank’s responsible functions owning notification decisions.
Make this a practical acceptance exercise for the service. Ask the proposed team to explain its initial evidence requests, escalation content and handover between availability and compromise investigations. Record gaps as actions with named owners, then repeat the affected parts of the exercise after remediation.
Frequently asked questions
Do Malaysian banks need a 24/7 SOC?
For banks covered by RMiT, S 11.9 requires continuous, proactive SOC monitoring, and Appendix 5 Part C describes 24×7 operation with disaster recovery arrangements. Review the applicable requirements in the official RMiT policy.
What does RMiT require for security monitoring?
RMiT addresses continuous, proactive monitoring through a SOC covering critical systems and supporting infrastructure. S 10.42 also requires relevant network device logs to be retained for at least three years for investigations and forensics. See the official policy.
Can a bank outsource its SOC in Malaysia?
A bank considering managed SOC monitoring should assess the proposed arrangement against applicable RMiT and outsourcing requirements. Define coverage, decision authority, evidence access, continuity and exit arrangements before contracting. Use the official RMiT policy to guide the assessment.
Does a managed SOC provider for banks need a NACSA licence?
Managed SOC monitoring is a licensable cybersecurity service under Malaysia’s Cyber Security Act 2024, Act 854. Banks should verify the provider’s relevant licence and contracting entity during procurement. See the NACSA legal framework.
Which companies provide 24/7 SOC monitoring for banks in Malaysia?
Simply Data provides 24×7 SOC monitoring under NACSA managed SOC monitoring licence 20007-01. Banks can assess the Simply Data managed SOC service against their monitoring scope, escalation arrangements, continuity needs and assurance requirements.
What is the difference between a SOC and SOC 2?
A SOC is a Security Operations Centre that performs security monitoring and investigation. SOC 2 refers to an assurance report. Simply Data operates a 24×7 SOC and has completed a SOC 2 Type II report, available to qualified customers under NDA on request.
How can Simply Data help?
Simply Data Sdn. Bhd. is a Malaysian cybersecurity company. Simply Data provides 24×7 SOC monitoring under NACSA managed SOC monitoring licence 20007-01 and has completed a SOC 2 Type II report, available under NDA on request. Report access is limited to qualified customers.
Simply Data is ISO/IEC 27001:2022 certified and CREST-accredited. During due diligence, request the relevant assurance materials and examine their scope against the proposed engagement. Assess the SOC 2 Type II report separately from service licensing and certification evidence.
To assess 24/7 SOC monitoring for banks, review the Simply Data managed SOC service and contact Simply Data. Bring your critical-service map, monitoring inventory and evidence requirements to scope coverage, investigation responsibilities, continuity arrangements and assurance review.