Malaysia’s industrial sectors face rising OT and ICS cyber threats. Learn how to secure operational technology, meet NACSA requirements, and protect critical infrastructure.
Malaysia’s industrial sectors face rising OT and ICS cyber threats. Learn how to secure operational technology, meet NACSA requirements, and protect critical infrastructure.
DFIR and ransomware incident response Malaysia retainer for rapid triage, evidence preservation, NACSA incident notification support and regulatory escalation planning.
Malaysia ransomware attacks H1 2026: top threat groups, hardest-hit sectors, ransom trends, and what Malaysian businesses must do now. Expert analysis from Simply Data.
Learn how digital forensics incident response (DFIR) works in Malaysia — NACSA 72-hour reporting, chain of custody, DFIR lifecycle, and what to look for in a DFIR provider.
Understand Malaysia Cyber Security Act 2024 penalties, NACSA licensing deadlines, 72-hour incident reporting, and NCII obligations. Expert compliance guide for Malaysian businesses.
A ransomware group reportedly claimed KTMB on a public leak site. Learn what Malaysian NCII operators must do under the Cyber Security Act 2024 — and a 6-step hardening checklist.
A proactive SOC eliminates attacker dwell time before an alert is ever generated — by hunting for threats continuously, running compromise assessments, and closing exposure windows before they are exploited. An agentic SOC automates response after detection. Both matter, but Malaysian businesses facing 21-day average dwell times in the banking sector need to ask the […]
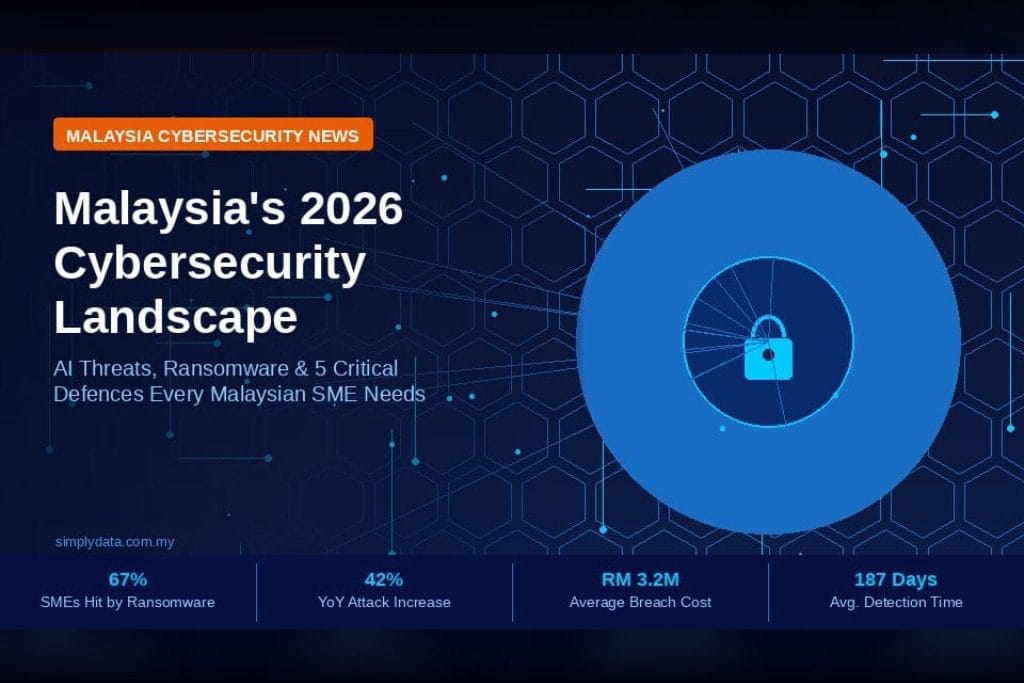
Malaysia cybersecurity 2026 is defined by the rapid evolution of AI-driven threats, deepfake social engineering, and increasingly sophisticated ransomware targeting SMEs. Understanding the landscape is the first step to building resilient defences. Malaysia’s 2026 Cybersecurity Landscape: What Changed, What’s New, and What You Must Do Malaysia’s cybersecurity landscape in 2026 looks dramatically different from 2024. […]
ISCB certified penetration testing Malaysia organisations can now access through Simply Data Sdn Bhd, following our achievement of Penetration Test Service Provider status from the Information Security Certification Body. Simply Data Sdn Bhd is proud to announce that we are now an officially ISCB Certified Penetration Test Service Provider (PTSP), awarded by CyberSecurity Malaysia under […]
CREST accreditation is an internationally recognised benchmark for vulnerability assessment quality. The Simply Data CREST accreditation for vulnerability assessment confirms our vulnerability assessments meet internationally recognised standards for technical rigour and professional conduct. Simply Data Sdn Bhd is honoured to announce that we have received CREST International certification in the Vulnerability Assessment category. This accreditation […]