Microsoft 365 Account Takeover in Malaysia: The Essential Guide to Credential Stuffing, OAuth Phishing and MFA Bypass
Protect Microsoft 365 accounts with practical checks for stolen passwords, malicious app consent, session theft and suspicious mailbox activity.
Binance hack lessons: what Malaysian businesses should learn
What Binance’s initial report on its October 2026 incident teaches Malaysian IT, SOC and leadership teams about developer targeting and internal AI access.
PHP2Shell Part 2: What Changed After the First Patch
PHP2Shell Part 2 covers what changed after the 21 October PHP fixes. It explains the narrow session upload progress advisory, the researcher claims, the NativePHP Mobile fixes that need app rebuilds and the Windows Brotli package rebuilds, and ends with a practical checklist.
Fortinet October 2026 Hardening: Why Patching, SOC Monitoring and VAPT Must Work Together
Fortinet announced a coordinated hardening release for 22 October 2026. This guide covers a practical checklist and selected 7.4 branch examples. It also explains how patching, SOC monitoring and VAPT retesting work together.
PHP2Shell: What Malaysian Businesses Should Patch, Test and Monitor
PHP fixed two critical PHP2Shell flaws on 21 October 2026. What Malaysian teams should patch, verify, test and monitor, and where each control stops.
Supply Chain Cyber Risk: How to Vet Third-Party Vendors in Malaysia
Learn how Malaysian organisations can vet third-party vendors with a proven TPRM framework covering ISO 27001, NACSA CSA, and BNM RMiT requirements. Protect your supply chain now.
Simply Data Wins PIKOM Digital Excellence Awards 2026 for Unified SOC Platform
Simply Data Sdn Bhd has been named a PIKOM Digital Excellence Awards 2026 winner for Managed Services — Unified SOC Platform, recognising SD Unified Platform and Agentic AI SOC capabilities.
Simply Data Completes SOC 2 Type II Report for Security, Confidentiality and Privacy
Simply Data has completed a SOC 2 Type II report covering Security, Confidentiality and Privacy. The confidential report is available to qualified customers under NDA/request.
Simply Data Listed as CSRO Licensed Provider & Cyber Trust Mark Advocate Tier 5
Simply Data is CSRO licensed in Singapore for penetration testing and managed SOC monitoring, and recognised at Cyber Trust Mark Advocate (Tier 5).
Simply Data Earns Anthropic Claude Certified Architect – Foundations (CCA-F) Certification
Simply Data Co-Founder Eric Leong passes the Anthropic CCA-F exam with 747/1000 — among Malaysia’s first Claude Certified Architects. What it means for AI-powered cybersecurity clients.

Simply Data Achieves ISCB Certified Penetration Test Service Provider (PTSP) Status
ISCB certified penetration testing Malaysia organisations can now access through Simply Data Sdn Bhd, following our achievement of Penetration Test Service Provider status from the Information Security Certification Body. Simply Data Sdn Bhd is proud to announce that we are now an officially ISCB Certified Penetration Test Service Provider (PTSP), awarded by CyberSecurity Malaysia under […]
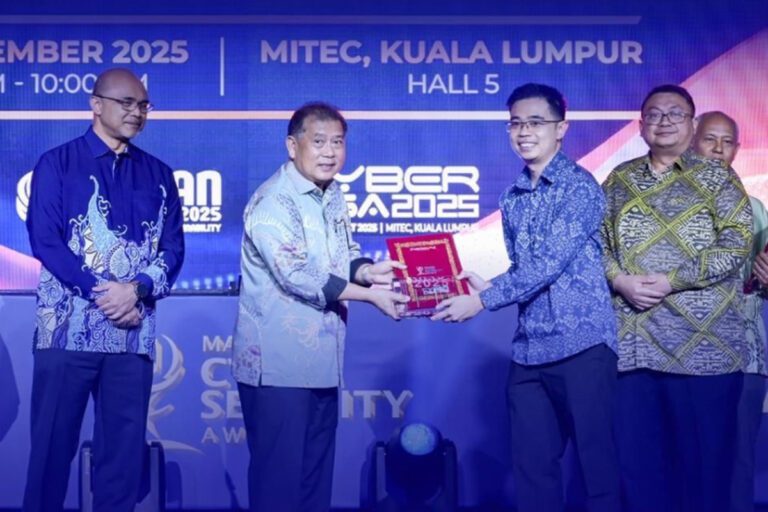
Simply Data Sdn. Bhd. Wins Cybersecurity Project of the Year at Malaysia Cybersecurity Awards 2025
Winning the cybersecurity award Malaysia 2025 for Project of the Year is a milestone that reflects our dedication to delivering exceptional security outcomes for Malaysian businesses. We are honoured to be recognised among the best in the industry. We are thrilled to announce that Simply Data Sdn. Bhd. has been awarded the Cybersecurity Project of […]
RMiT Appendix 12 and NCII Compliance: What Malaysian Banks Should Check
BNM added the NCII Code of Practice in September 2026. Review applicability, provider licences and evidence alongside existing RMiT controls.
PDPA 2026 Year in Review: Key Enforcement Actions and What’s Coming in 2027
PDPA Malaysia 2026 enforcement review: breach notifications, penalties, DPO obligations, and what 2027 regulation means for your business.
ISO 27001 vs SOC 2 vs PCI DSS: Which Certification Does Your Malaysian Business Need?
Side-by-side comparison of ISO 27001, SOC 2 and PCI DSS for Malaysian businesses: scope, audience, certification process and which to pursue based on your industry.
Bank Negara RMiT Compliance: A Cybersecurity Checklist for Malaysian Financial Institutions
BNM Risk Management in Technology policy guide: control domains, SOC monitoring expectations, third-party risk, and incident reporting. Checklist for Malaysian banks.

Cyber Security Act 2024 Malaysia: NACSA Licensing Deadlines and Penalties Explained
Understand Malaysia Cyber Security Act 2024 penalties, NACSA licensing deadlines, 72-hour incident reporting, and NCII obligations. Expert compliance guide for Malaysian businesses.

SC Malaysia Cybersecurity Guidelines: What Capital Market Players Must Do in 2026
The SC Malaysia cybersecurity guidelines set out mandatory security requirements for capital market participants — stockbrokers, fund managers, investment advisers, and market infrastructure operators. What you must do in 2026.
Typosquatting in Malaysia: Spot Fake Shops Before 11.11 and 12.12
A practical guide for Malaysian businesses to detect typosquatting, fake shops and cloned pages around 11.11 and 12.12, and to respond with evidence.
Cybersecurity Budget Planning for 2027: Where Malaysian Businesses Should Invest
Plan your 2027 cybersecurity budget with confidence. A risk-based guide for Malaysian businesses covering SOC, VAPT, DFIR, compliance, and NACSA CSA requirements.
OT and ICS Security in Malaysia: Protecting Industrial Control Systems
Malaysia’s industrial sectors face rising OT and ICS cyber threats. Learn how to secure operational technology, meet NACSA requirements, and protect critical infrastructure.
Network Security Hardening: A Configuration Audit Checklist for Malaysian SMEs
Practical network hardening checklist for Malaysian SMEs: firewall rules, network segmentation, default credentials, patch management and what a professional audit adds.
Building a Cyber Incident Response Retainer: Why Speed Matters in Malaysia
DFIR and ransomware incident response Malaysia retainer for rapid triage, evidence preservation, NACSA incident notification support and regulatory escalation planning.
Managed SOC vs In-House SOC in Malaysia: Cost, Coverage and 24/7 Reality
Managed SOC vs in-house SOC in Malaysia: compare operating models, 24/7 coverage, AI detection and RMiT compliance to make the right choice.

Dark Web Monitoring for Malaysian Businesses: How to Detect Leaked Data Early
Discover how dark web monitoring helps Malaysian businesses detect leaked credentials, PII, and card data early — before attackers exploit them. Learn more.

Managed Security Services Malaysia: How to Choose the Right MSSP for Your Business
Choosing the right managed security services Malaysia provider is one of the most critical cybersecurity decisions a business can make. A quality MSSP delivers 24/7 threat monitoring, incident response, and expert security operations.

What Is MDR? Managed Detection and Response Malaysia 2026 — Complete Guide
Managed Detection and Response (MDR) gives your organisation 24/7 threat monitoring, rapid incident response, and expert security operations — without the cost of building an in-house SOC. Complete Malaysia guide for 2026.