Skip to content
  • Case Studies
  • Cybersecurity Readiness Assessment
simply data logo
  • About
    • About Us
    • Innovation
      • SD Platform Overview
    • Certifications & Awards
  • Our Services
    • CyberSecurity Services
      • DFIR (Digital Forensics and Incident Response)
      • Compromise Assessment
      • Security Operations Center (SOC) Managed Service
        • SD-Cyber Deception
        • Threat Intelligence
        • Managed Detection and Response (MDR)
        • Cloud Security Posture Management (CSPM)
        • Web Defacement Monitoring
        • In-house Automation Script Development
        • Advanced Malware Analysis & Threat Intelligence
        • Office 365 Monitoring
        • SaaS Monitoring
      • Extended Threat Intelligence
        • Dark Web Monitoring
        • Attack Surface Management
        • Cyber Risk Management
        • Supply Chain Intelligence
      • Security Posture Assessment (SPA)
      • VAPT & Penetration Testing
      • Network & Security Configuration Audit & Hardening
      • Phishing Email Simulation
      • SOAR Security Services
      • OT Cybersecurity Services
      • Managed Security Service Provider (MSSP)
    • Managed Network & Security Services
    • Application Performance Monitoring (APM)
      • APM as a Service (APMaaS)
      • Cloud Monitoring
      • Database Performance Monitoring
      • Web Application Monitoring
      • Synthetic Testing Monitoring
      • Real User Monitoring (RUM)
      • Application Stress Test / Load Test Services
    • Consultancy Services
      • NCSB Risk Assessment
      • Security BluePrint™ Consultancy Services
    • Agentic AI & Automation
      • SD Unified Platform (SDP)
      • Agentic AI SOC
      • AI Automation
      • SD Monitoring — 100% Data Ingestion Visibility | SD Unified Platform
      • SDP-Portal — Customer-Facing SOC Visibility | SD Unified Platform
      • AI Threat Hunting — Chat-Driven Investigation by SD Unified Platform
    • Supported Platform
      • TrendAI Vision One
    CyberSecurity Services
    • VAPT & Penetration Testing
    • Cyber - 911 - DFIR Services
    • Compromise Assessment
    • Security Operations Center (SOC)
    • Extended Threat Intelligence
    • Security Posture Assessment (SPA) Services
    • Network & Security Configuration Audit & Hardening
    • Phishing Email Simulation
    • AI Automation
    • OT Cyber Security
    • SOAR Security
    • MSSP (Managed Security Service Provider)
    Managed Network & Security Services
    • Managed Network & Security Services
    Consultancy Services
    • NCSB Risk Assessment
    • Security BluePrint™ Consultancy Services
    Agentic AI & Automation
    • SD Unified Platform
    • Agentic AI SOC
    • AI Automation
    • SD Monitoring
    • SDP-Portal
    • AI Threat Hunting
    Application Performance Monitoring
    • APM as a Service (APMaaS)
    • Cloud Monitoring
    • Database Performance Monitoring
    • Web Application Monitoring
    • Synthetic Testing Monitoring
    • Real User Monitoring (RUM)
    • Stress Test / Load Test – Performance Assessment
    Supported Platform
    • TrendAI Vision One

    Not Sure What Security Threats Your Organization is Facing?

    We can help. Contact us now for a free consultation and protect your business from potential risks.

    Contact Us
  • Technology Vendor Partners
  • Blog & News
  • Contact
    • Contact Us
    • Become a Simply Data Partner

Under Attack?

Submit your message through our contact form or call us at +603 5886 2714.

    SIEM

    • Home
    • SIEM
    siem explained malaysia
    Industry Insights & Trends

    SIEM Explained: How Security Information and Event Management Powers Your SOC

    October 10, 2026

    Learn how SIEM works, why BNM RMiT mandates centralised logging, and how Simply Data SOC uses SIEM to detect threats for Malaysian enterprises. Read now.
    Malaysia Cybersecurity Threat Report 2025
    Industry Insights & Trends

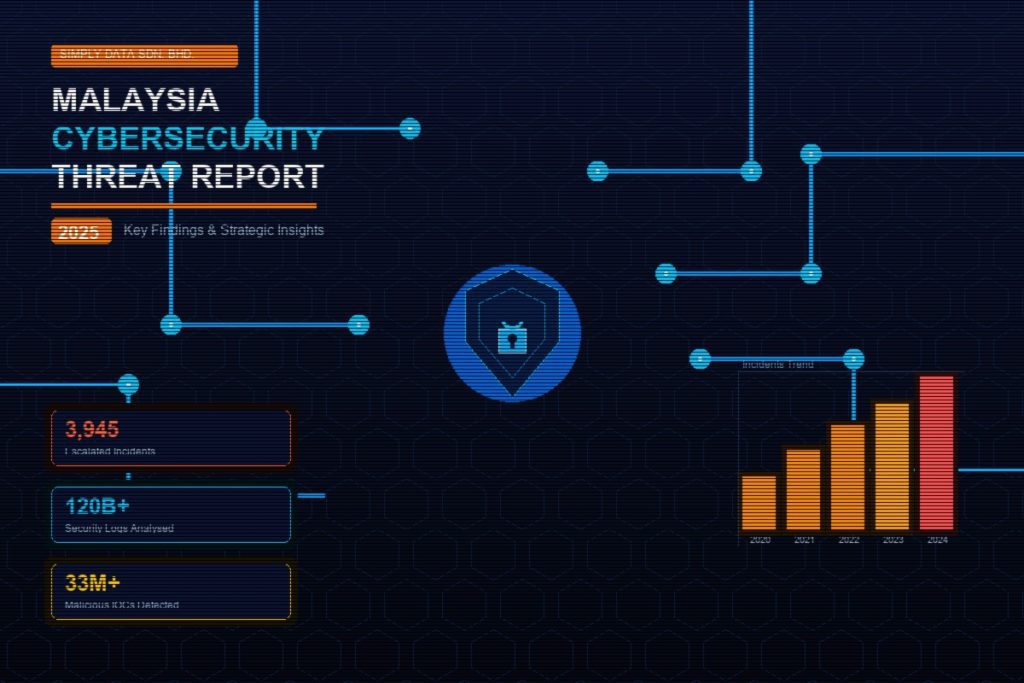
    Malaysia Cybersecurity Threat Report 2025: Key Findings & Strategic Insights

    February 27, 2026

    Simply Data 2025 Malaysia Cybersecurity Threat Report analyses 120B+ security logs, 3,945 escalated incidents, and 33M+ malicious IOCs. Discover the top threats targeting Malaysian organisations and what to do now.
    What Is Threat Intelligence In Cyber Security
    Cybersecurity Tips

    What Is Threat Intelligence In Cyber Security

    April 7, 2025

    Threat intelligence cybersecurity Malaysia organisations leverage is the practice of collecting, analysing, and acting on information about current and emerging cyber threats. For Malaysian businesses, effective threat intelligence is the foundation of a proactive security posture. With the advancement and continuously evolving cyber threats, organizations can no longer afford to rely solely on reactive security […]
    What Is Security Operation Center (SOC) In Cyber Security
    Cybersecurity Tips

    What Is Security Operation Center (SOC) In Cyber Security?

    April 7, 2025

    A Security Operations Center Malaysia businesses and enterprises rely on is a centralised team of cybersecurity professionals who monitor, detect, analyse, and respond to cyber threats around the clock. Understanding how a SOC works is essential for any organisation considering managed security services. A Security Operations Center (SOC), or sometimes called an information security operations […]
    The Role of Automation in Modern Security Operations Centers (SOC)
    Cybersecurity Tips

    The Role of Automation in Modern Security Operations Centers (SOC)

    March 26, 2025

    SOC automation Malaysia security teams are embracing is reshaping threat detection and incident response. From automated alert triage to orchestrated response workflows, automation is becoming a core capability of any modern Security Operations Centre in Malaysia. Cybersecurity is no longer just about detecting threats—it’s about responding to them quickly and effectively. In a world where […]
    How Real Time Threat Intelligence Enhances Your SOC’s Effectiveness
    Cybersecurity Tips

    How Real-Time Threat Intelligence Enhances Your SOC’s Effectiveness

    March 26, 2025

    Real-time threat intelligence SOC Malaysia teams rely on is the foundation of effective, proactive cyber defence. By feeding current threat data directly into security monitoring workflows, Malaysian SOCs can detect sophisticated attacks faster and respond with greater precision. In the ever-evolving landscape of cybersecurity, having access to real-time threat intelligence is a game-changer. With cyber […]
    The Role of SIEM in a Modern Security Operations Center
    Cybersecurity Tips

    The Role of SIEM in a Modern Security Operations Center

    March 26, 2025

    SIEM security operations Malaysia teams use as a foundational technology provides centralised visibility across all security events. By correlating log data from multiple sources, SIEM enables SOC analysts to identify complex attack patterns that would otherwise go undetected. In today’s digital world, data is one of a company’s most valuable assets. But as businesses increasingly […]
    SOC integrates with cybersecurity tools — Simply Data managed SOC integration Malaysia
    Cybersecurity Tips

    How SOC Integrates with Your Existing Cybersecurity Tools to Improve Protection

    March 26, 2025

    A Security Operations Centre (SOC) integrates with your existing cybersecurity tools by collecting alerts and logs from firewalls, endpoint protection, antivirus and other systems in one place, where analysts correlate them and coordinate the response. This improves protection without replacing the tools you already own, because the SOC adds context, continuous monitoring and response on […]
    Hand Touching Cyber Protection Interface: Data Privacy and Security Concept
    Cybersecurity Tips

    SOC Threat Hunting: What It Is and How It Helps Prevent Cyberattacks

    March 26, 2025

    SOC threat hunting Malaysia security teams practise is a proactive approach to cybersecurity that goes beyond automated detection. Rather than waiting for alerts, skilled threat hunters actively search for signs of compromise that may have evaded automated defences. As cyber threats become more advanced and frequent, organizations need to take a proactive approach to defending […]
    Proactive Threat Detection in SOC Malaysia - Simply Data Cybersecurity
    Cybersecurity Tips

    The Importance of Proactive Threat Detection in Your SOC

    March 26, 2025

    Proactive threat detection Malaysia security teams practise recognises that the most damaging cyberattacks often go undetected for weeks or months. By moving from a reactive to a proactive security posture, Malaysian businesses can dramatically reduce the impact of successful intrusions. Cyber threats are becoming more sophisticated, and traditional reactive security measures are no longer enough […]

    Posts pagination

    1 2 Next

    Search

    Categories

    • Announcements (12)
    • Cybersecurity Tips (47)
    • Industry Insights & Trends (24)
    • Regulatory & Compliance (11)
    • Service Spotlight (17)

    Recent posts

    • network security hardening checklist malaysia
      Network Security Hardening: A Configuration Audit Checklist for Malaysian SMEs
    • ot ics security malaysia
      OT and ICS Security in Malaysia: Protecting Industrial Control Systems
    • PIKOM Digital Excellence Awards 2026 Unified SOC Platform winner announcement by Simply Data
      Simply Data Wins PIKOM Digital Excellence Awards 2026 for Unified SOC Platform

    Tags

    2026 Trends AI Cybersecurity AI Threats apm Bank Negara RMiT Bursa Malaysia Certification Company News Compliance Cost-Benefit Analysis cyber-security-act cybersecurity-malaysia cybersecurity compliance Cybersecurity Malaysia Cyber SOC Cyber Threats DDoS Dwell Time Incident Response iso27001 Malaysia Malaysia Cybersecurity 2025 Managed Services Managed SOC MDR nacsa Network Security PDPA penetration-testing Proactive Cybersecurity Ransomware Regulatory ROI SIEM SME Budget SME Security soc stockbrokers threat-intelligence Threat Hunting Threat Report Unified SOC Platform vapt Web Application Security XDR
    simply data logo

    Started in 2022, Simply Data is a CREST certified and NACSA Licensed (No. 20007-01 & 20007-02) Cyber Security company in Malaysia that provides cyber security services including Network & Security IT Managed Service, Security Operation Centre (SOC), Cyber Threat Intelligence, Vulnerability Assessment & Penetration Testing (VAPT) service, Application Performance Monitoring (APM) services, and more.

    • B-03A-03, 3RD Floor, Block B Setiawalk, Persiaran Wawasan, Pusat Bandar Puchong, 47160 Puchong, Selangor
    • +603 5886 2714
    • contactus@simplydata.com.my

    Quick Links

    • Home
    • About Us
    • Innovation
    • Technology Vendor Partners
    • Blog / News
    • Career Opportunities
      Hiring
    • Become a Simply Data Partner
    • Cybersecurity Readiness Assessment
    • Malaysia CyberSecurity Act 854

    CyberSecurity Services

    • Cyber - 911 - DFIR Services
    • Compromise Assessment
    • Security Operations Center (SOC)
    • Extended Threat Intelligence
    • Security Posture Assessment (SPA) Services
    • Network & Security Configuration Audit & Hardening
    • Phishing Email Simulation

    Managed Network & Security Services

    • Managed Network & Security Services

    Observability Application Performance Monitoring

    • Observability APM as a Service
    • Cloud Monitoring
    • Database Performance Monitoring
    • Web Application Monitoring
    • Synthetic Testing Monitoring
    • Real User Monitoring
    • Stress Test / Load Test – Performance Assessment

    Consultancy Services

    • NCSB Risk Assessment
    • Security BluePrint™ Consultancy Services

    © 2026 Simply Data Sdn Bhd. All rights reserved.

    • Terms & Conditions
    • Data Protection & User Privacy
    • Privacy Policy
    • Cookie Policy