Cybersecurity Business Case: Cost Drivers and ROI for Malaysian SMEs
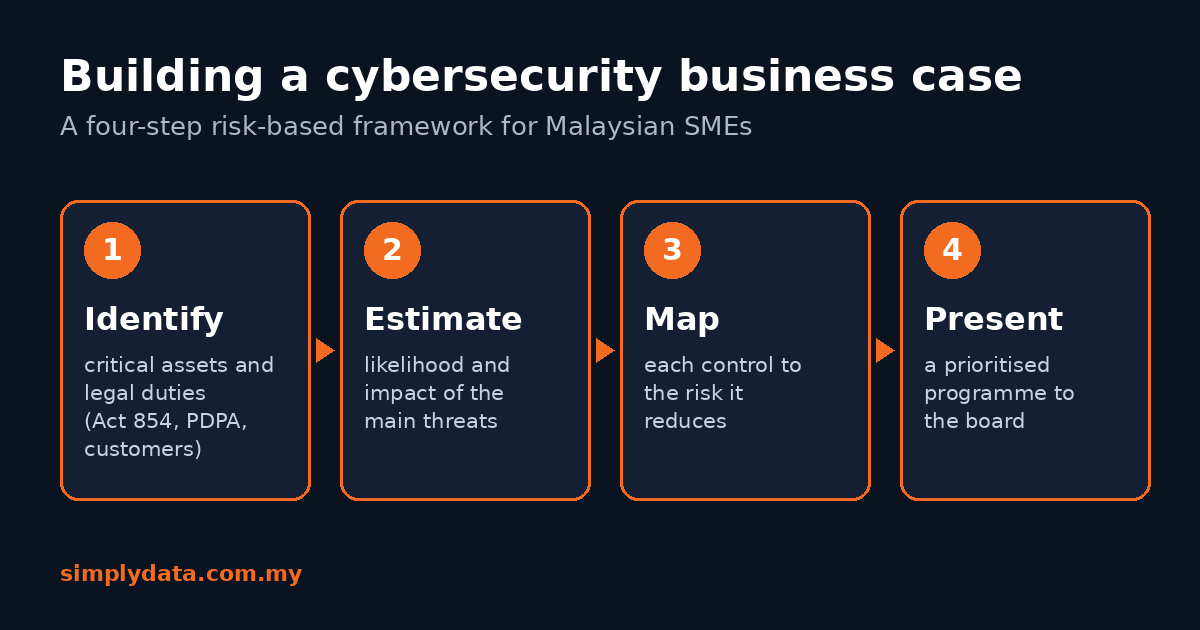
A cybersecurity business case for a Malaysian SME should be built around risk, not price. Simply Data recommends identifying critical assets and legal duties, estimating how likely and damaging the main threats are, and showing how each control reduces that risk.
Present the outcome as a prioritised programme linked to applicable legal duties and customer requirements. Confirm whether Act 854 designation or licensing requirements apply to your organisation, then obtain a scoped proposal.
Why does the cybersecurity business case matter now?
Three pressures have moved cybersecurity from an IT line item to a board-level decision.
Regulation has tightened. The Cyber Security Act 2024 (Act 854) places duties on national critical information infrastructure (NCII) entities, including risk assessments, audits, compliance with codes of practice and incident notification, with penalties that vary by offence. It also requires providers of managed security operations centre (SOC) monitoring and penetration testing services to be licensed by the National Cyber Security Agency (NACSA). SMEs that supply NCII organisations increasingly inherit these expectations through contracts and supplier assessments.
The Personal Data Protection Act 2010, as amended in 2024, provides for a fine of up to RM1,000,000, imprisonment of up to three years, or both, for breaching the Personal Data Protection Principles. The amendments also introduced mandatory data breach notification and data protection officer requirements, subject to the applicable notification criteria and appointment thresholds. Suppliers to financial institutions face further scrutiny under Bank Negara Malaysia’s Risk Management in Technology (RMiT) policy.
Threats keep evolving. Ransomware, business email compromise and credential theft continue to target Malaysian organisations of every size, as our Malaysia Threat Report 2024 and 2026 cybersecurity landscape guide explain. Include ransomware, business email compromise and credential theft in your risk assessment.
Expectations have risen. In its August 2024 forecast, Gartner projected worldwide end-user spending on information security to reach USD 212 billion in 2025. Customers, insurers and auditors now expect evidence of security controls, and a clear business case is how you decide which ones to fund.
What drives the cost of a cybersecurity programme?
Cost is shaped by scope, not by a standard list. Understanding the drivers helps you scope sensibly and compare proposals like for like.
- Scope and critical assets: the number of sites, business systems, cloud tenancies and applications to be protected or tested.
- Log sources and data volume: how many firewalls, servers, cloud services and applications feed the monitoring platform, and how much data they generate.
- Endpoints and users: the laptops, servers, mobile devices and identities that need detection, response and access controls.
- Coverage hours: business-hours monitoring versus round-the-clock (24/7) detection and response, and the response times you require.
- Compliance obligations: Act 854 codes of practice, the PDPA, RMiT, ISO/IEC 27001 or customer audits, each adding reporting, log retention and evidence work.
- Testing depth and frequency: how many applications, networks and APIs are assessed, and how often.
- Skills: whether you need analysts, incident responders, threat hunters, penetration testers or compliance specialists, and for how long.
How do you quantify cyber risk for an ROI framework?
Return on security investment is measured in risk avoided rather than revenue earned. A four-step framework keeps the analysis credible without demanding perfect data.
1. Which assets matter most?
List the systems and data the business depends on, such as the ERP, customer database or e-commerce platform, and rate the consequence of losing confidentiality, integrity or availability for each.
2. How likely is each threat?
Use incident history, threat reports and a security posture assessment to judge how likely each threat is over the next year.
3. What impact would an incident have?
Consider downtime, recovery effort, regulatory exposure, contractual penalties, lost customers and reputational harm. Ask finance and operations colleagues to validate the estimates.
4. How much risk would each control reduce?
Reassess likelihood and impact assuming each proposed control is in place. The difference is the risk reduction the investment buys.
What is annualised loss expectancy (ALE)?
Where data allows, express risk in money using annualised loss expectancy. ALE multiplies the single loss expectancy (the expected loss from one incident) by the annual rate of occurrence (how often that incident is expected each year). Calculate ALE before and after a control to estimate the annual reduction in expected loss. To calculate return on security investment, subtract the annualised control cost from that reduction, then divide by the annualised control cost. Use your own figures, because industry averages rarely reflect an individual SME.
Where monetary data is thin, a semi-quantitative register works well. Score likelihood and impact from 1 (low) to 5 (high) and multiply them:
| Risk | Likelihood | Impact | Inherent score | Proposed control | Residual score |
|---|---|---|---|---|---|
| Ransomware on file servers | 4 | 5 | 20 | 24/7 SOC monitoring and tested offline backups | 8 |
| Exploitable flaw in customer portal | 3 | 4 | 12 | Vulnerability assessment, penetration testing and patching | 4 |
| Business email compromise | 4 | 3 | 12 | Email security, multi-factor authentication and awareness training | 6 |
The scores are illustrative prioritisation aids, not measured probabilities or financial returns. Record the residual likelihood and impact behind each residual score and explain the assumptions. Then attach costs from scoped proposals.
Should you build an in-house team or use a managed service?
The right operating model depends on capability, coverage and control. The comparison below covers the factors boards most often raise.
| Factor | In-house team | Managed service |
|---|---|---|
| Skills | Recruit and retain analysts, responders and testers in a competitive market | Access to a multidisciplinary team across detection, response and testing |
| Coverage | 24/7 cover needs shift rotation and enough staff to absorb leave and turnover | Confirm monitoring hours, response responsibilities and escalation arrangements in the service agreement |
| Time to capability | Hiring, tooling and process design take time to mature | People, platforms and processes already exist; onboarding follows scoping |
| Tooling | You select, integrate and maintain SIEM, EDR and threat intelligence | The provider operates the platforms and threat intelligence |
| Governance and control | Direct control over people, processes and data | Control through contracts, service levels, reporting and audit rights |
| Regulatory fit | Internal policies must align with Act 854, the PDPA and sector rules | Managed SOC monitoring and penetration testing providers must hold NACSA licences under Act 854 |
| Scalability | Adding coverage means further recruitment | Scope adjusts as the business changes |
Many SMEs choose a hybrid: an internal owner who sets priorities, manages risk and governs the provider, supported by a managed security operations centre for monitoring and response. What is SOC as a Service? explains how this works, and our cybersecurity services, penetration testing and APM as a Service pages describe the options.
When assessing providers, ask for evidence rather than claims. Simply Data is licensed by NACSA for Managed SOC Monitoring (20007-01) and Penetration Testing (20007-02). Simply Data is also CREST-accredited for Vulnerability Assessment, is certified to ISO/IEC 27001:2022 and has completed a SOC 2 Type II report, available under NDA.
How should you present the business case to the board?
Boards approve investments they understand. Use this checklist:
- State the business objective: protecting revenue, meeting customer requirements or achieving compliance.
- List the obligations that apply: Act 854, the PDPA, RMiT, ISO/IEC 27001 or contractual clauses.
- Show the top risks in a register with likelihood, impact and an owner for each.
- Explain the proposed controls and the risk reduction each delivers.
- Compare operating models on skills, coverage, time to capability, tooling and governance.
- Present a phased roadmap with clear milestones.
- Define success measures, such as time to detect and respond, patching timeliness and audit findings closed.
- State the residual risk the board is being asked to accept.
- Attach scoped proposals so costs reflect your actual environment.
Frequently Asked Questions
What affects the cost of a managed SOC?
The cost of a managed SOC depends mainly on scope: the number of log sources and endpoints, daily data volume, coverage hours, log retention period and the response services included. Compliance reporting under Act 854 or the PDPA, and any custom detection use cases, also shape the effort. A scoped assessment of your environment sets it.
How do I calculate the ROI of cybersecurity?
Estimate annualised loss expectancy for each key risk by multiplying the expected loss from one incident by its expected annual frequency. Recalculate with the control in place to estimate the annual reduction in expected loss. Subtract the annualised control cost from that reduction, then divide by the annualised control cost to calculate return on security investment.
Should an SME build an in-house security team or use a managed service?
A hybrid model is one option: an internal owner sets priorities, manages risk and governs suppliers, while a managed provider delivers agreed services such as 24/7 monitoring, incident response and specialist testing. A full in-house team needs scarce skills, shift cover and tooling. Compare the options on skills, coverage, time to capability, tooling and governance.
Does the Cyber Security Act 2024 apply to SMEs?
The Cyber Security Act 2024 (Act 854) applies directly to designated national critical information infrastructure entities and to providers of licensable cybersecurity services. Most SMEs are not designated, but those supplying NCII organisations often face similar requirements through contracts and supplier audits. Choosing NACSA-licensed providers for managed SOC monitoring and penetration testing helps meet these expectations.
What should a cybersecurity business case include?
A cybersecurity business case should include the business objective, applicable legal and contractual obligations, a prioritised risk register, proposed controls with the risk reduction each delivers, a comparison of operating models, a phased roadmap, success measures and the residual risk the board must accept. Costs should come from scoped proposals that reflect your environment rather than generic estimates.
What is the next step?
A credible business case links security investment to the risks and obligations your board already cares about. Start with your critical assets and legal duties, quantify risk using the framework above, and compare operating models on capability. Then obtain a proposal built around your actual scope.
Contact Simply Data Sdn. Bhd. for a scoped proposal covering managed SOC monitoring, vulnerability assessment and penetration testing for your environment.
References
- Gartner, Information Security Spending Forecast: https://www.gartner.com/en/newsroom/press-releases/2024-08-28-gartner-forecasts-global-information-security-spending-to-grow-15-percent-in-2025
- Bank Negara Malaysia, Risk Management in Technology (RMiT): https://www.bnm.gov.my/-/pd-rmit-nov25