Simply Data: CSRO Licensed Cybersecurity Service Provider Singapore, Cyber Trust Mark Advocate (Tier 5)
Simply Data is now a Licensed Cybersecurity Service Provider in Singapore. The Cybersecurity Services Regulation Office (CSRO), under the Cyber Security Agency of Singapore (CSA), has licensed Simply Data under the Cybersecurity Act 2018 for penetration testing and managed security operations centre (SOC) monitoring. Simply Data is also recognised at Cyber Trust Mark Advocate (Tier 5), the highest of the five Cyber Trust Mark tiers.
For Singapore organisations searching for a CSRO licensed cybersecurity service provider Singapore buyers can verify, this gives a clear answer: Simply Data holds two CSRO licences for the two licensable cybersecurity services and is listed at the highest Cyber Trust Mark tier.
What Simply Data has achieved in Singapore
Simply Data has achieved two important Singapore milestones: CSRO licensing for regulated cybersecurity services and Cyber Trust Mark Advocate (Tier 5) recognition.
- Penetration testing: licensed by CSRO under licence CS/PTS/C-202609-1161.
- Managed security operations centre (SOC) monitoring: licensed by CSRO under licence CS/SOC/C-202609-1162.
- Published CSRO list: Simply Data appears on CSRO’s published list of licensed business entities dated 2 Oct 2026.
- Cyber Trust Mark: on the CSRO list dated 9 Oct 2026, Simply Data is recognised at Cyber Trust Mark Advocate (Tier 5).
These achievements matter because they connect service licensing, customer assurance and cybersecurity governance in one provider. Singapore organisations can engage Simply Data for security testing and SOC monitoring with licence numbers that procurement, risk and compliance teams can record and verify.
CSRO licensed cybersecurity service provider Singapore: Licensed Cybersecurity Service Provider
Singapore’s Cybersecurity Act 2018 created a licensing framework for cybersecurity services that require trusted access to customer systems. Penetration testing and managed SOC monitoring are the two licensable services. Both are high-trust activities: penetration testers assess applications, networks and infrastructure, while SOC teams monitor security events and alerts across customer environments.
Choosing a licensed provider gives Singapore buyers a stronger procurement basis. It shows that the provider is licensed for the service being delivered, appears on a public CSRO list and can give your internal stakeholders clear evidence for vendor due diligence.
- Procurement confidence: licence numbers give sourcing teams a clear record for supplier evaluation.
- Audit support: risk and compliance teams can document that regulated services are delivered by a CSRO licensed provider.
- Service clarity: the licence categories match the services customers buy: penetration testing and managed SOC monitoring.
- Board visibility: leadership teams can see that high-trust cybersecurity work is assigned to a recognised provider.
For organisations that operate in Singapore, a CSRO licensed cybersecurity service provider Singapore teams can verify supports more confident decisions across procurement, technology, governance and risk.
Cyber Trust Mark tiers explained
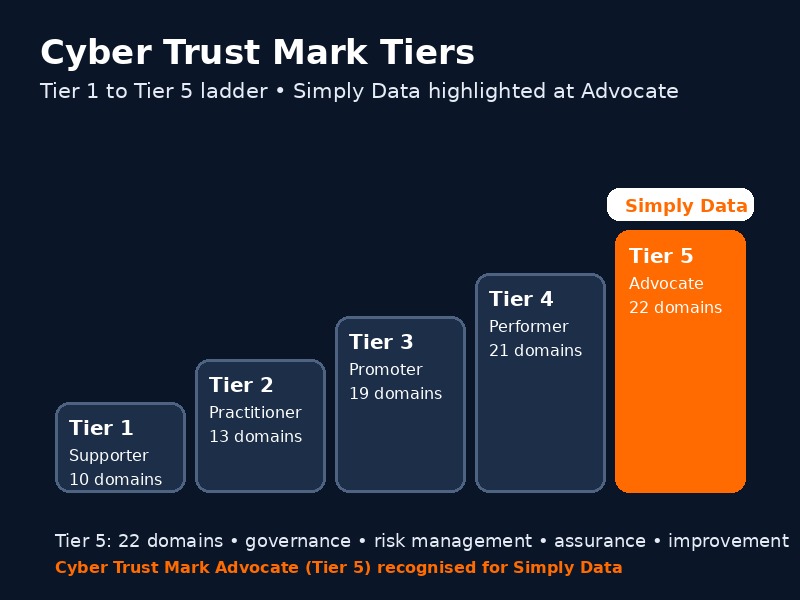
The Cyber Trust Mark has five tiers. Each tier covers a defined number of cybersecurity domains, from Tier 1 Supporter through to Tier 5 Advocate. Tier 5 Advocate is the highest tier and covers all 22 domains, including full cybersecurity governance, risk management, assurance and continuous improvement.
| Tier | Name | Domains | What it means |
|---|---|---|---|
| Tier 1 | Supporter | 10 | Cybersecurity practices across 10 domains. |
| Tier 2 | Practitioner | 13 | Expanded cybersecurity practices across 13 domains. |
| Tier 3 | Promoter | 19 | Broader cybersecurity coverage across 19 domains. |
| Tier 4 | Performer | 21 | Advanced cybersecurity coverage across 21 domains. |
| Tier 5 | Advocate – Simply Data | 22 | Full cybersecurity governance, risk management, assurance and continuous improvement across all 22 domains. |
Simply Data Tier 5 Advocate recognition gives customers a strong signal that the company has reached the top Cyber Trust Mark tier. It also aligns with what customers expect from a security provider: mature governance, disciplined risk management, assurance and continuous improvement.
What Tier 5 Advocate means for customers
Cyber Trust Mark Advocate (Tier 5) is meaningful for customers because it covers all 22 cybersecurity domains. It reflects full cybersecurity governance, risk management, assurance and continuous improvement.
For customers, this means the provider responsible for testing or monitoring your environment is also operating with a high level of cybersecurity maturity in its own organisation. That supports stronger supplier assurance, easier risk review and more confident stakeholder conversations.
- Governance: cybersecurity is managed with clear ownership and direction.
- Risk management: security priorities are tied to structured risk thinking.
- Assurance: evidence supports customer, audit and procurement discussions.
- Continuous improvement: practices keep improving as threats, technology and customer needs evolve.
Services covered: penetration testing, managed SOC and MDR
Simply Data Singapore CSRO licences cover two service lines that organisations use to strengthen resilience: penetration testing and managed SOC monitoring.
Penetration testing
Simply Data penetration testing service helps organisations identify exploitable weaknesses across applications, networks and infrastructure. Testing gives security leaders clear findings, prioritised remediation actions and evidence that can support risk, compliance and executive reporting.
Managed SOC and MDR
Simply Data Managed SOC provides security monitoring for organisations that need visibility, alert triage and analyst-led investigation. Customers that want detection and response support can also explore Managed Detection and Response (MDR).
These services work together: penetration testing helps find weaknesses before they are exploited, while SOC and MDR support continuous monitoring, detection and response. See the broader Simply Data services portfolio for related cybersecurity support.
What this means for Singapore customers
For Singapore customers, the practical value is straightforward. You can appoint one provider for security validation, monitoring and response conversations with a clear CSRO licensing record. Security teams can focus on scope, risk and remediation. Procurement teams can capture licence numbers in supplier files. Compliance teams can point to the CSRO list and the Cyber Trust Mark Tier 5 recognition when documenting vendor assurance.
The combination is especially useful when a project needs both a point-in-time assessment and ongoing visibility. A penetration test identifies weaknesses that require action. Managed SOC monitoring and MDR help the organisation watch for suspicious activity, triage alerts and respond with structure. When both services come from the same licensed provider, customers get a more joined-up view of risk, evidence and operational security.
Simply Data Singapore recognition also supports regional teams that manage cybersecurity across multiple markets. A Singapore buyer can verify CSRO licences and Cyber Trust Mark Tier 5 status. A Malaysia buyer can see the same provider’s NACSA licences in the home market. This makes supplier conversations cleaner for organisations that want strong assurance, responsive service delivery and a partner with recognised credentials across the region.
For management teams, this creates a concise assurance story: two CSRO licences, Tier 5 Advocate recognition and service coverage across testing, monitoring and MDR. The same facts can be reused in board papers, supplier registers and customer security questionnaires. That reduces friction during reviews and helps teams move from credential checking to the work that matters: improving security outcomes.
The outcome is simple: Singapore organisations get verified licensing, highest-tier Cyber Trust Mark recognition and a practical service path for security testing, monitoring and response across Singapore operations and regional assurance reviews confidently.
How to verify Simply Data on CSRO
Singapore organisations can verify Simply Data directly through CSRO. Visit https://www.csro.gov.sg/ and check the published list of licensed business entities.
- Open the CSRO website.
- Find the published list of licensed business entities.
- Look for Simply Data on the list dated 2 Oct 2026.
- Check the penetration testing licence CS/PTS/C-202609-1161.
- Check the managed SOC monitoring licence CS/SOC/C-202609-1162.
- Check the list dated 9 Oct 2026 for Cyber Trust Mark Advocate (Tier 5) recognition.
This gives procurement, compliance and security teams a simple verification path before appointing a provider for regulated cybersecurity services.
Our Malaysia home market
Simply Data is also NACSA-licensed in Malaysia under the Cyber Security Act 2024 (Act 854), with MSOC licence 20007-01 and Pentest licence 20007-02. Simply Data also holds ISO/IEC 27001:2022 and CREST. Customers can also request Simply Data SOC 2 Type II assurance report under NDA.
Frequently asked questions
What is CSRO?
CSRO is Singapore’s Cybersecurity Services Regulation Office under the Cyber Security Agency of Singapore. CSRO licenses providers for penetration testing and managed SOC monitoring under the Cybersecurity Act 2018.
Is Simply Data licensed by CSRO in Singapore?
Yes. Simply Data is licensed for penetration testing under CS/PTS/C-202609-1161 and managed SOC monitoring under CS/SOC/C-202609-1162.
What does Cyber Trust Mark Advocate (Tier 5) mean?
Advocate is the highest of the five Cyber Trust Mark tiers. Tier 5 covers 22 domains and represents full cybersecurity governance, risk management, assurance and continuous improvement.
How can my team verify Simply Data CSRO licences?
Visit csro.gov.sg and check the CSRO published list of licensed business entities. Simply Data appears on the list dated 2 Oct 2026, and Tier 5 Advocate recognition appears on the list dated 9 Oct 2026.
Which services should Singapore organisations discuss with Simply Data?
Singapore organisations can discuss penetration testing, Managed SOC and MDR with Simply Data. These services support security validation, continuous monitoring, detection and response.
Speak with Simply Data
If your organisation needs a CSRO licensed cybersecurity service provider Singapore teams can verify for penetration testing, Managed SOC or MDR, Simply Data is ready to support you.
Contact Simply Data today through https://www.simplydata.com.my/contact/ to discuss your requirements with our team.