- Home
- CyberSecurity Services
- Security Operations Center (SOC) Managed Service
NACSA-Licensed Managed SOC Malaysia | AI-Powered MDR & SIEM
Managed Security Operations Centre (SOC) is a 24/7 service delivered by a NACSA-licensed cybersecurity service provider for monitoring, detection, SIEM, SOAR and incident response coordination across endpoints, networks, cloud and business applications. Simply Data supports SOC provider Malaysia requirements, SOC services Kuala Lumpur and nationwide delivery, and MDR Malaysia as an optional/package-dependent capability under one managed SOC service.

Managed SOC Malaysia: SOC Provider, MDR and SIEM Services
Simply Data provides NACSA-licensed managed SOC services for Malaysian organisations that need continuous monitoring, threat detection, response coordination, optional MDR support and evidence-backed cybersecurity operations.
Recognised by CyberSecurity Malaysia
Simply Data was awarded Cybersecurity Project of the Year 2025 at the Malaysia Cybersecurity Awards 2025 by CyberSecurity Malaysia (MITEC, Kuala Lumpur) — in recognition of a nationwide SOC Monitoring deployment covering real-time log ingestion, SIEM migration, SOAR automation and SD Unified Platform across one of Malaysia’s largest AWS infrastructures.

INTELLIGENCE REPORT
Malaysia Cybersecurity Threat Report 2025
Simply Data annual analysis of the Malaysian cyber threat landscape — ransomware trends, phishing campaigns, sector-specific risks, and threat actor activity targeting Malaysian organisations.
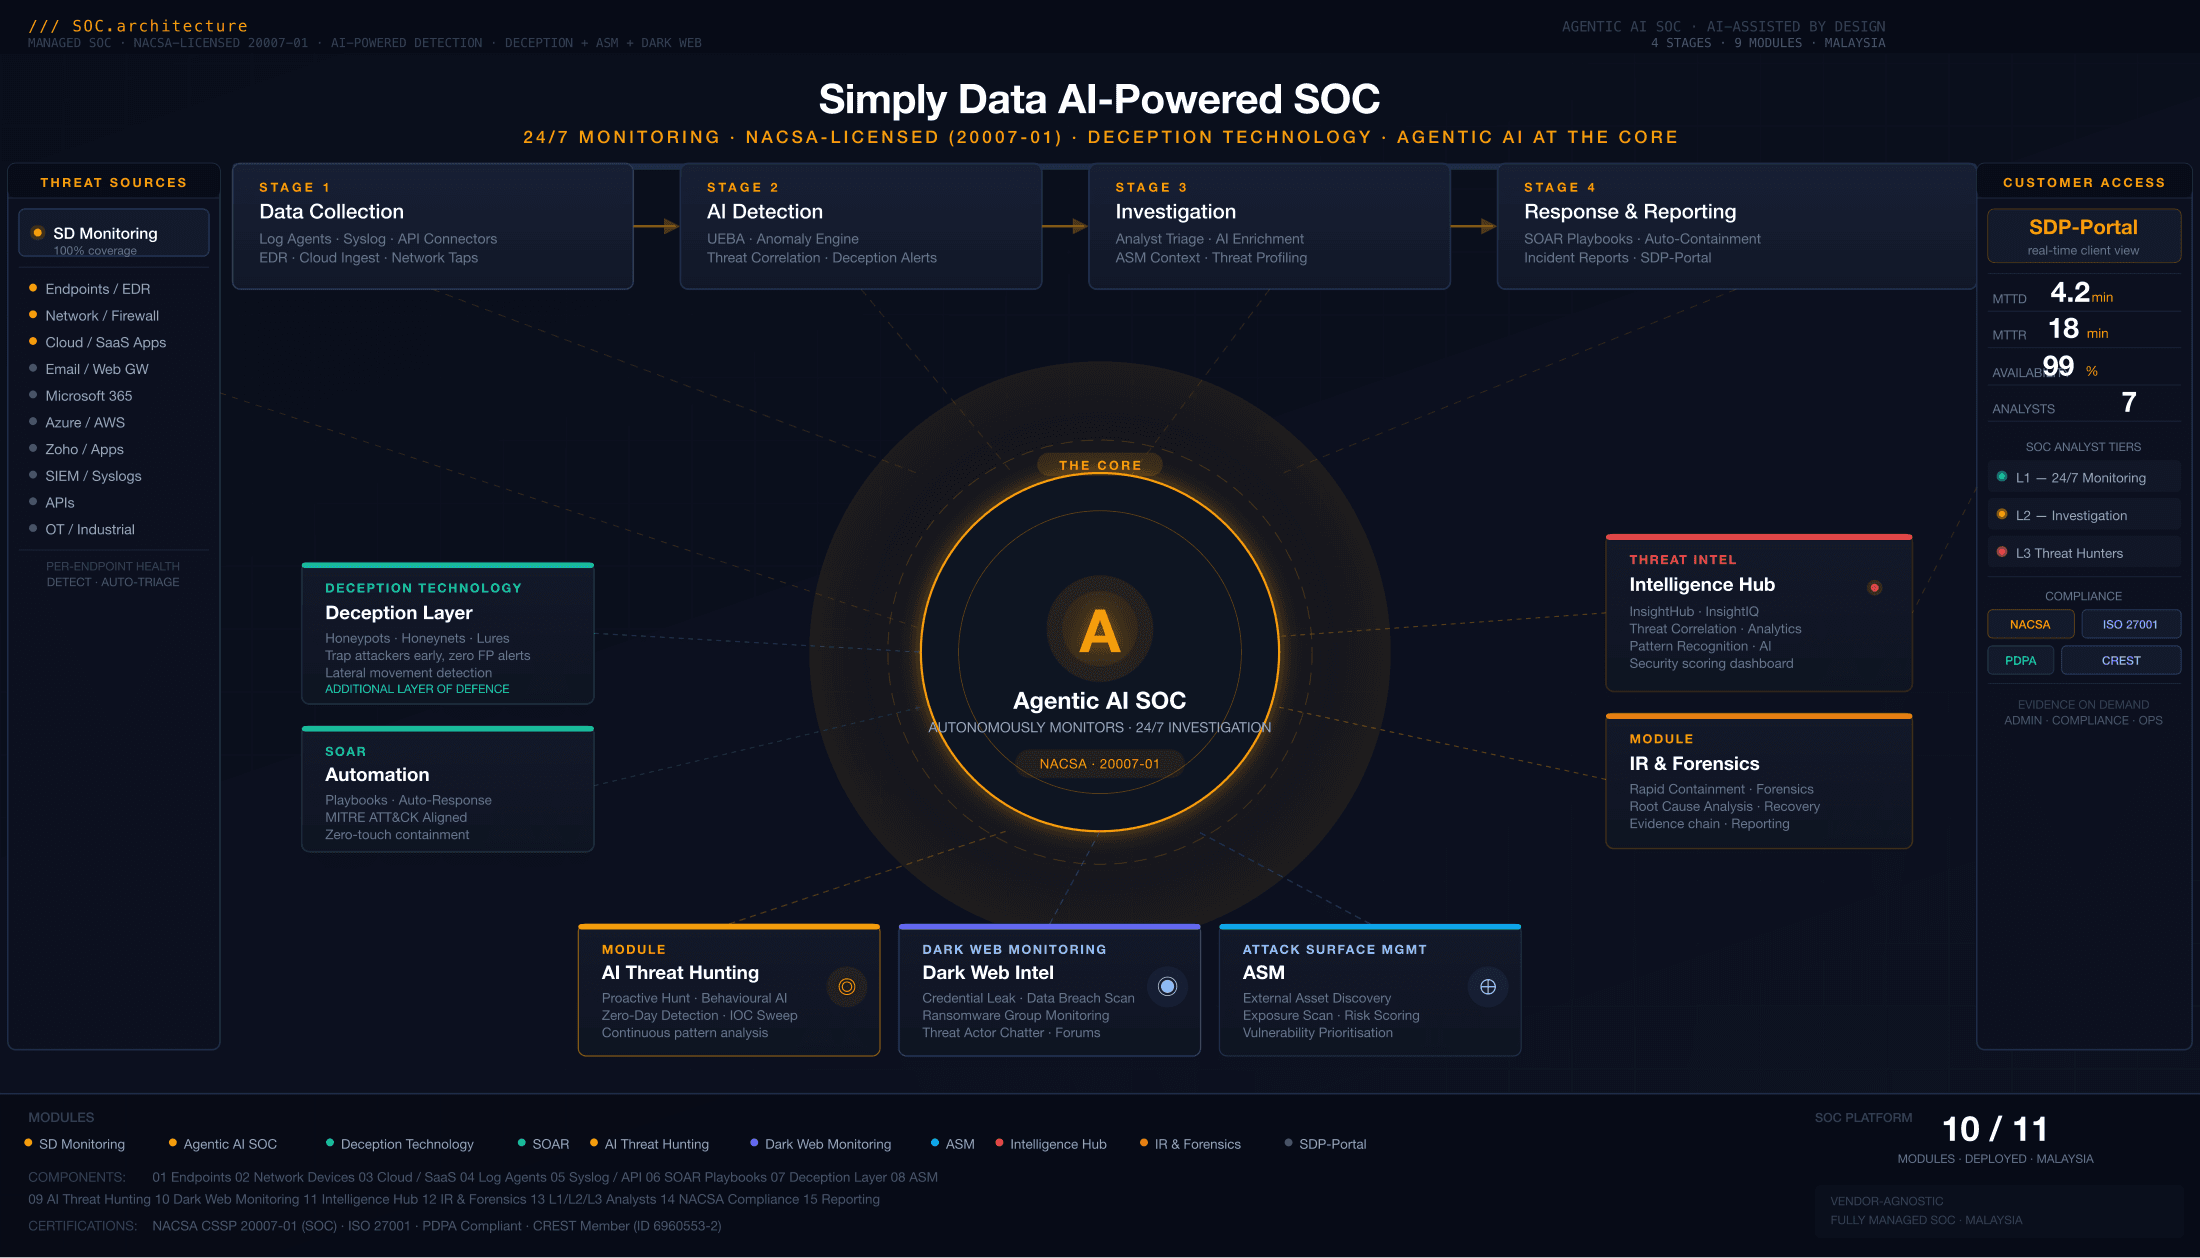
SOC ARCHITECTURE AND DESIGN
Our SOC Package
| SOC Features / Optional Items | SD Sentinel Contact Us | SD Guardian Contact Us | SD Vanguard Contact Us |
|---|---|---|---|
| 24x7 Security Monitoring | ✔ | ✔ | ✔ |
| Threat Intelligence Integration | ✔ | ✔ | ✔ |
| 24x7 Incident Response | ✔ | ✔ | ✔ |
| Reporting (Weekly, Monthly, Incident Reporting) | ✔ | ✔ | ✔ |
| Early Warning System (EWS) Newsletter | ✔ | ✔ | ✔ |
| Active Threat Hunting with Machine Learning | ✘ | ✔ | ✔ |
| Automated Blocking on Firewall (SOAR) | ✘ | ✔ | ✔ |
| Attack Surface Management / Dark Web Monitoring / Brand Monitoring | ✘ | Lite Version | ✔ |
| Logs Retention | 3 Months | 6 Months | 1 Year |
| Endpoint / Server Remediation | ✘ | ✔ | ✔ |
| M365 / SaaS Monitoring Module | ✘ | ✔ | ✔ |
| Security Auditing using CIS and NIST Benchmark | ✘ | ✔ | ✔ |
| Web Defacement Monitoring | ✘ | ✔ | ✔ |
| File Integrity Monitoring (FIM) | ✘ | ✔ | ✔ |
| Compliance Reporting (PCI-DSS, ISO 27001, RMiT, etc) | ✘ | ✘ | ✔ |
| External Vulnerability Assessment & Penetration Testing | ✘ | ✘ | ✔ |
| Managed Detection and Response (MDR) | ✘ | ✘ | ✔ |
| Cloud Security Posture Management (Cloud Infra Monitoring) | ✘ | ✘ | ✔ |
| Customised Automation (Based on Use Case) | ✘ | ✘ | ✔ |
| Malware Analysis Module | ✘ | ✘ | ✔ |
| SD-Deception Technology (Honeypots / Honeytokens)– NEW | ✘ | ✘ | ✔ |
| UEBA (User & Entity Behavior Analytics) | ✘ | ✘ | ✔ |
SD Sentinel
- ✔ 24x7 Security Monitoring
- ✔ Threat Intelligence Integration
- ✔ 24x7 Incident Response
- ✔ Reporting (Weekly, Monthly, Incident Reporting)
- ✔ Early Warning System (EWS) Newsletter
- ✘ Active Threat Hunting with Machine Learning
- ✘ Automated Blocking on Firewall (SOAR)
- ✘ Attack Surface Management / Dark Web Monitoring / Brand Monitoring
- ✔ Logs Retention: 3 Months
- ✘ Endpoint / Server Remediation
- ✘ M365 / SaaS Monitoring Module
- ✘ Security Auditing using CIS and NIST Benchmark
- ✘ Web Defacement Monitoring
- ✘ File Integrity Monitoring (FIM)
- ✘ Compliance Reporting (PCI-DSS, ISO 27001, RMiT, etc)
- ✘ External Vulnerability Assessment & Penetration Testing
- ✘ Managed Detection and Response (MDR)
- ✘ Cloud Security Posture Management (Cloud Infra Monitoring)
- ✘ Customised Automation (Based on Use Case)
- ✘ Malware Analysis Module
- ✘ SD-Deception Technology (Honeypots / Honeytokens)
- ✘ UEBA (User & Entity Behavior Analytics)
SD Guardian
- ✔ 24x7 Security Monitoring
- ✔ Threat Intelligence Integration
- ✔ 24x7 Incident Response
- ✔ Reporting (Weekly, Monthly, Incident Reporting)
- ✔ Early Warning System (EWS) Newsletter
- ✔ Active Threat Hunting with Machine Learning
- ✔ Automated Blocking on Firewall (SOAR)
- ✔ Lite Version: Attack Surface Management / Dark Web Monitoring / Brand Monitoring
- ✔ Logs Retention: 6 Months
- ✔ Endpoint / Server Remediation
- ✔ M365 / SaaS Monitoring Module
- ✔ Security Auditing using CIS and NIST Benchmark
- ✔ Web Defacement Monitoring
- ✔ File Integrity Monitoring (FIM)
- ✘ Compliance Reporting (PCI-DSS, ISO 27001, RMiT, etc)
- ✘ External Vulnerability Assessment & Penetration Testing
- ✘ Managed Detection and Response (MDR)
- ✘ Cloud Security Posture Management (Cloud Infra Monitoring)
- ✘ Customised Automation (Based on Use Case)
- ✘ Malware Analysis Module
- ✘ SD-Deception Technology (Honeypots / Honeytokens)
- ✘ UEBA (User & Entity Behavior Analytics)
SD Vanguard
- ✔ 24x7 Security Monitoring
- ✔ Threat Intelligence Integration
- ✔ 24x7 Incident Response
- ✔ Reporting (Weekly, Monthly, Incident Reporting)
- ✔ Early Warning System (EWS) Newsletter
- ✔ Active Threat Hunting with Machine Learning
- ✔ Automated Blocking on Firewall (SOAR)
- ✔ Attack Surface Management / Dark Web Monitoring / Brand Monitoring
- ✔ Logs Retention: 1 Year
- ✔ Endpoint / Server Remediation
- ✔ M365 / SaaS Monitoring Module
- ✔ Security Auditing using CIS and NIST Benchmark
- ✔ Web Defacement Monitoring
- ✔ File Integrity Monitoring (FIM)
- ✔ Compliance Reporting (PCI-DSS, ISO 27001, RMiT, etc)
- ✔ External Vulnerability Assessment & Penetration Testing
- ✔ Managed Detection and Response (MDR)
- ✔ Cloud Security Posture Management (Cloud Infra Monitoring)
- ✔ Customised Automation (Based on Use Case)
- ✔ Malware Analysis Module
- ✔ SD-Deception Technology (Honeypots / Honeytokens) – NEW
- ✔ UEBA (User & Entity Behavior Analytics)
Key Features of Simply Data Security Operations Center (SOC) Service
24/7 Real-Time Monitoring
Continuous, around-the-clock monitoring of your network and systems.
Vendor-Agnostic SIEM
Supports customized log collection and analysis from any system, regardless of the vendor.
Local & Global Threat Intelligence
Integration of both local and global threat intelligence to detect emerging threats.
Automated Threat Detection & Response
Swift identification and automatic blocking of malicious activities with SOAR technology.
Optional Data Recovery
Assistance with data or system recovery can be provided as an optional service.
Compliance Assistance
Helps your business meet regulatory compliance requirements with automated monitoring and reporting.
What Makes Up a Security Operations Center?
A successful security operations center is built upon three foundational pillars which are People, Processes, and Technology, that must work in harmony to deliver effective cyber resilience.

People: The Human Element
The core of any security operations center is its skilled team. These roles include:
- Security Analysts The frontline responders who monitor alerts, triage incidents, and investigate suspicious activity.
- Security Engineers Specialists responsible for designing, deploying, and maintaining the security tools and infrastructure (like the SIEM and firewalls).
- SOC Managers The leaders who set strategy, manage resources, coordinate major incident response efforts, and align the security operations center goals with the overall business strategy.

Processes: The Playbook
Defined workflows ensure consistent and efficient responses to threats. These processes govern how the managed SOC Malaysia operates:
- Triage and Prioritization Categorizing alerts by severity (e.g., high, medium, low) to ensure the most dangerous threats are addressed first.
- Incident Containment Procedures to quickly isolate infected systems and minimize the damage of a confirmed attack.
- Forensic Analysis and Remediation Steps taken after an incident are contained to understand the root cause, clean up the environment, and fix the underlying vulnerability to prevent recurrence.

Technology: The Tool Stack
The following platforms power our managed SOC Malaysia stack, designed to meet the requirements of the Bursa Malaysia Guidance on Management of Cyber Risks and equivalent Malaysian regulations:
- SIEM Collects, aggregates, and correlates security logs from all sources to detect patterns.
- EDR/XDR Monitors endpoints (laptops, servers) to detect and respond to threats at the device level.
- SOAR Automates repetitive tasks and orchestrates complex responses (like automatically blocking an IP address).
How Does Security Operations Center (SOC) Work?
Our SOC operates using a multi-layered strategy to offer comprehensive protection for your business. Here's how we deliver superior security monitoring and response:
01.
Continuous 24/7 Monitoring
We provide round-the-clock security monitoring to ensure that your systems are constantly under surveillance. Our team collects and analyzes logs from various devices and platforms, from cloud services to on-premise systems. With real-time detection, we can immediately respond to security threats and minimize the potential impact on your business.
02.
Vendor-Agnostic Core Engine (SIEM)
One of the key features of our SOC is its vendor-agnostic Security Information and Event Management (SIEM) system. Unlike other security services that are restricted by vendor-specific log collection requirements, our SIEM platform allows us to customize log integrations. This flexibility ensures that we can monitor and analyze data from any vendor or device, tailoring the solution to fit your specific infrastructure.
03.
Threat Intelligence Integration
Our SOC integrates local Threat Intelligence gathered from Malaysia's unique cybersecurity landscape. By collaborating with local telecommunication service providers, we maintain a locally developed threat intelligence database, offering insights into regional threats and ensuring the highest relevance and accuracy for Malaysia-based organizations.
04.
Automated Threat Detection and Response (SOAR)
Simply Data SOC incorporates Security Orchestration, Automation, and Response (SOAR) technology to automate the detection and response to threats. This significantly reduces response time and minimizes the risk of human error. Some of the key automation features include:
- Automated Blocklisting Integration with firewalls (Sangfor, Fortinet, Palo Alto, Cisco, Sophos, etc.) to automatically generate blocklists based on IP reputation. Suspicious IPs are flagged and blocked immediately, preventing further threats.
- Dynamic Quarantine Malicious IP addresses are placed in quarantine, with automatic unblocking when the IP is recycled or deemed safe after a specified period.
05.
Incident Response & Optional Data Recovery
In the event of a security breach, our SOC team immediately springs into action to contain the threat, investigate its root cause, and initiate the response process. While data or system recovery is optional and not included in our core SOC services, we work closely with recovery teams should you require assistance.
- Identification Quickly identify the nature and scope of the attack.
- Containment Prevent the attack from spreading further across your systems.
- Eradication Remove any malicious files, malware, or unauthorized access.
- Post-Incident Analysis We conduct forensic analysis to understand how the attack occurred and improve future defenses.
06.
Compliance Monitoring
Our SOC services are designed to help your business stay in compliance with industry regulations and standards such as GDPR, ISO 27001, PCI-DSS, and HIPAA. By continuously monitoring your network and providing detailed reports, we ensure that you meet all the necessary compliance requirements for your industry.
Key Sub-Services Bundled in
Simply Data Managed SOC Offering

SD-Cyber Deception
A unique part of our SOC, providing an added layer of protection by deceiving attackers with decoy systems and detecting threats early in their lifecycle.
View More

Threat Intelligence
Bundled in our SOC offering, providing both local and global threat intelligence to enhance your defense against cyber threats.
View More

Managed Detection & Response (MDR)
Available as an optional service, where we help manage your EDR tools and fine-tune security policies to ensure optimal protection.
View More

Cloud Security Posture Management (CSPM)
An optional service to maintain and strengthen the security posture of your cloud infrastructure.
View More

Web Defacement Monitoring
Bundled in our SOC service, we actively monitor and protect against any potential web defacement attacks to your website.
View More

SOAR In-House Automation
Bundled automation blocking integration with any brand, and any number of firewalls (e.g., Fortinet, Palo Alto, Cisco, Sophos, etc.) for SOC contract customers. We automatically generate and send blocklists based on bad IP reputation, significantly improving your defense.
View More

Advanced Malware Analysis
Bundled in our SOC offering, we analyze and investigate malware attacks, providing real-time intelligence to improve threat detection and mitigation.
View More

Office 365 Monitoring
Simply Data Managed SOC ensures robust Office 365 monitoring to detect and mitigate risks before they impact your business.
View More

SaaS Monitoring
Simply Data Managed SOC delivers advanced SaaS monitoring to protect your data, applications, and users, ensuring security and compliance at all times.
View More
Benefits of Simply Data SOC Service
Proactive Defense
Our SOC service gives you peace of mind by proactively detecting threats before they cause harm.
Faster Response Times
Automated threat detection and expert-led response teams ensure minimal downtime.
Customizable Solutions
Tailored log collection and analysis, ensuring the solution fits your unique needs.
Cost-Effective
Save resources by outsourcing to a specialized SOC team while getting access to advanced security tools.
Reduced Risk
By identifying and responding to threats in real-time, our SOC service reduces the risk of data breaches and financial losses.
Powered by SD Unified Platform — Simply Data AI SOC Engine
Simply Data Managed SOC runs on the SD Unified Platform (SDP) — the Simply Data Agentic AI SOC engine. SDP automates the investigation workflow across four modules:
- Agentic AI SOC — AI agents assist L1 triage and draft L2 investigations for analyst review
- AI Threat Hunting — Chat-driven threat investigation via SD Unified Platform
- SDP-Portal — Customer-facing SOC visibility dashboard
- SD Monitoring — 100% data ingestion visibility
Frequently Asked Questions
A Managed Security Operations Centre is a 24/7 service that monitors security events, detects suspicious activity and coordinates incident response. Simply Data Managed SOC combines SIEM, SOAR, threat intelligence, analyst review and AI-assisted investigation to help Malaysian organisations detect and respond to cyber threats faster.
Yes. Simply Data holds Malaysian cybersecurity service-provider licensing for Managed Security Operations Centre monitoring. This supports customers that need a local, regulated SOC provider for Malaysian cybersecurity and procurement requirements.
Yes. Simply Data is listed in Singapore's official CSRO licensed business entities list for managed SOC monitoring and penetration testing. In the official CSRO list dated 9 Oct 2026, Simply Data appears under the Cyber Trust Mark Advocate (Tier 5) section for the relevant licensed service categories.
A Security Operations Centre is an operational cybersecurity service that monitors, detects and responds to threats. SOC 2 Type II is a separate assurance report over controls. Simply Data provides managed SOC services and has separately completed a SOC 2 Type II report that is available to qualified customers under NDA/request.
Simply Data Managed SOC can include SIEM monitoring, alert triage, threat intelligence, SOAR automation, MDR investigation support, reporting and escalation workflows. Scope depends on the customer environment, monitored assets, compliance requirements and response model.
SIEM collects and correlates logs. MDR adds managed detection, investigation and response. Managed SOC is the operating model that brings people, process and platform together for continuous monitoring and response. Simply Data links these capabilities through the SD Unified Platform.
Managed SOC is most relevant for regulated organisations, companies with sensitive data, organisations operating critical systems, and teams that need continuous monitoring but do not want to build a full in-house SOC. It is also useful when internal IT teams need stronger threat detection and incident response coverage.
Start with a consultation and environment review. Simply Data will confirm the systems to monitor, data sources, escalation contacts, compliance needs, reporting format and response workflow before proposing the SOC/MDR scope.
Simply Data provides managed SOC services in Malaysia from its Malaysian operations, supporting organisations that need 24/7 monitoring, SIEM correlation, MDR investigation support, escalation workflows and reporting to support compliance evidence. The service is designed for Malaysian regulated organisations and regional teams that need a local SOC provider.
Simply Data Managed SOC covers 24/7 monitoring, SIEM correlation, analyst review and escalation. MDR adds investigation and response support, using threat intelligence and AI-assisted investigation workflows, with analysts reviewing escalations. Scope depends on the agreed service package and monitored environment.
Get Your Free
Consultation Now!
We’re here to help! Contact us to learn more about our Security Operations Center (SOC) managed services!
- B-03A-03, 3RD Floor, Block B Setiawalk, Persiaran Wawasan, Pusat Bandar Puchong, 47160 Puchong, Selangor
- +603 5886 2714
- contactus@simplydata.com.my
Agentic AI SOC. Sovereign Malaysian infrastructure.
SDP unifies 11 SOC modules — Agentic AI SOC, AI Threat Hunting, SDP-Portal, SD Monitoring, and more — in one role-aware workspace. NACSA-licensed (20007-01) under the Cyber Security Act 2024.
Managed SOC in Action — Real Client Results
See how Simply Data Managed SOC has protected leading Malaysian organisations across government, judiciary, and enterprise sectors.
Managed Security for National Judiciary
Full L1–L3 managed SOC deployment protecting a national judiciary organisation — 24/7 monitoring, incident response, and compliance reporting.
Managed SOC for Large Conglomerate
Enterprise-wide managed SOC covering multiple business units — threat detection, SIEM integration, and MDR for a large Malaysian conglomerate.
SOC for Large Government Agency
Nation-scale managed SOC deployment for a major Malaysian government agency — continuous monitoring across critical infrastructure.