- Home
- CyberSecurity Services
- Cybersecurity Compliance Services in Malaysia: PDPA, Cyber Security Act 2024 (NCII) and BNM RMiT
Cybersecurity Compliance Services in Malaysia
PDPA, Cyber Security Act 2024 (NCII) and BNM RMiT: technical controls, monitoring and testing from a NACSA-licensed provider
Cybersecurity compliance services for PDPA, the Cyber Security Act 2024 and BNM RMiT
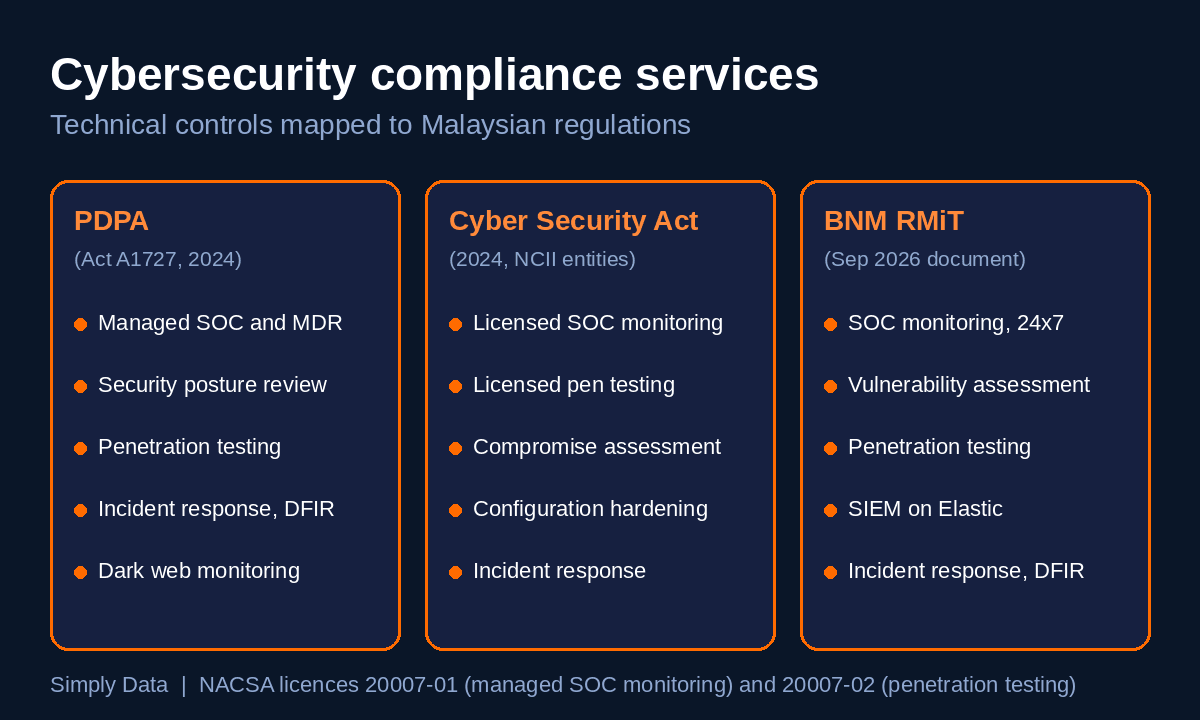
Simply Data Sdn Bhd provides technical cybersecurity compliance services in Malaysia for the Personal Data Protection Act 2010 (PDPA), the Cyber Security Act 2024 and Bank Negara Malaysia’s Risk Management in Technology (RMiT) policy: technical controls, monitoring, testing and evidence. We hold NACSA licences under the Cyber Security Act 2024 for managed SOC monitoring and penetration testing.
We do not provide legal advice. We work alongside your legal counsel, DPO and auditors, and legal interpretation stays with them.
What our cybersecurity compliance services cover
- 24×7 security monitoring and detection through our SOC and MDR services
- Penetration testing and vulnerability assessment of networks, web, mobile, cloud and IoT
- Security posture assessments and network configuration audits that feed your risk assessments and audits
- SIEM on Elastic (SD Unified Platform)
- Incident response and digital forensics to support regulatory notifications
- Threat intelligence, including dark web monitoring and attack surface management
- Reports and records that your DPO, compliance team and auditors can use
How do we support PDPA compliance?
The Personal Data Protection (Amendment) Act 2024 (Act A1727) came into force in phases on 1 January, 1 April and 1 June 2025. Since 1 June 2025, a data controller must notify the Personal Data Protection Commissioner of a personal data breach as soon as practicable.
The Data Breach Notification Guidelines set a 72-hour notification period and explain when the clock starts in discovery and confirmation scenarios.
Where a breach causes or is likely to cause significant harm, the controller must also notify affected data subjects without unnecessary delay, and no later than 7 days after the initial notification to the Commissioner. The Security Principle now applies directly to data processors.
Controllers and processors that meet the thresholds in the DPO guidelines must appoint a Data Protection Officer.
| Requirement or technical objective | Simply Data service |
|---|---|
| Security Principle: protect personal data held by controllers and processors | Security Posture Assessment, penetration testing, network configuration audit and hardening, CSPM |
| Support breach detection and investigation for notification under the Data Breach Notification Guidelines | Managed SOC 24×7, MDR |
| Establish the facts of a breach for the notification to the Commissioner and to data subjects | Cyber incident response, DFIR |
| Find exposed personal data and credentials outside your network | Dark web monitoring, attack surface management |
| Reduce the risk of breaches caused by phishing | Phishing email simulation |
How do we help NCII entities comply with the Cyber Security Act 2024?
The Cyber Security Act 2024 (Act 854) came into force on 26 August 2024. It places duties on national critical information infrastructure (NCII) entities across 11 sectors, including banking and finance, energy, healthcare services, and water, sewerage and waste management.
Under the 2024 regulations, an NCII entity must carry out a cyber security risk assessment at least once a year and a cyber security audit at least once every two years, or more often if NACSA’s Chief Executive directs.
Under the incident notification regulations, the entity must notify electronically immediately when the incident becomes known, provide particulars within 6 hours and send supplementary information within 14 days of the initial notification.
These services support your own risk assessment, audit and incident-response processes. A penetration test, compromise assessment or configuration review is not, by itself, the statutory risk assessment or audit.
| Requirement or technical objective | Simply Data service |
|---|---|
| Technical input to the cyber security risk assessment required at least once a year | Security Posture Assessment, compromise assessment |
| Technical evidence for the cyber security audit required at least once every two years | Network configuration audit and hardening, penetration testing |
| Notify incidents immediately when known, with particulars within 6 hours | Managed SOC 24×7, MDR, cyber incident response |
| Send supplementary information within 14 days after the initial notification | DFIR |
| Providers of managed SOC monitoring and penetration testing services must hold a licence under the Act | NACSA-licensed managed SOC and penetration testing |
| Protecting operational technology in NCII sectors | OT cybersecurity (IEC 62443) |
How do we support BNM RMiT compliance?
Bank Negara Malaysia’s Risk Management in Technology (RMiT) policy document sets technology risk requirements for financial institutions. The current version was issued on 25 September 2026 and adds the NACSA-endorsed NCII Code of Practice as Appendix 12.
RMiT expects continuous SOC monitoring of critical systems, regular vulnerability assessment and penetration testing, and retention of relevant network device logs for investigations and forensics for at least three years.
| Requirement or technical objective | Simply Data service |
|---|---|
| S 11.9 and Appendix 5 Part C: continuous, proactive SOC monitoring of critical systems and supporting infrastructure, operating 24×7 | Managed SOC 24×7, MDR |
| S 10.42: retain relevant network device logs for investigations and forensics for at least three years | SIEM on Elastic (SD Unified Platform), with log sources, retention period, storage and retrieval scoped and agreed for each engagement |
| Appendix 5 Part D: quarterly vulnerability assessment of network components supporting critical systems | Vulnerability assessment and penetration testing |
| Appendix 5 Part D: annual intelligence-led penetration testing covering network infrastructure, critical systems and digital services, and testing before introducing new systems for new products or services | Penetration testing, attack surface management and dark web monitoring |
| Incident reporting under the relevant BNM policy documents | Cyber incident response, DFIR |
BNM incident reporting timelines depend on the policy document that applies. Institutions under the Business Continuity Management policy must notify BNM within 2 hours of confirming a cyber incident disruption. Under Operational Risk Reporting, cyber incidents and events, including near misses, must be reported within T+14 calendar days of confirmation, and any earlier deadline takes priority.
Your compliance team confirms which obligations apply to you, and we provide the technical facts. For an example of this work, see our security compliance hardening case study for a financial institution.
What we do not do
We provide technical services only. To keep roles clear:
- We do not give legal advice on PDPA, the Cyber Security Act 2024, RMiT or any other law. Your legal counsel handles legal interpretation.
- We do not act as your Data Protection Officer. We give your DPO the technical reports and incident facts they need.
- We do not carry out certification audits as a certification body, and we do not issue ISO/IEC 27001 certificates.
- We do not decide whether you comply. That decision rests with your regulators, auditors and counsel.
Why organisations choose Simply Data for regulated environments
- NACSA licences under the Cyber Security Act 2024: 20007-01 Managed SOC Monitoring and 20007-02 Penetration Testing
- ISO/IEC 27001:2022 certified
- CREST-accredited
- CyberSecurity Malaysia (ISCB) Penetration Test Service Provider (PTSP)
- SOC 2 Type II report completed; available to qualified customers under NDA/request
- Malaysia Cybersecurity Awards 2025: Cybersecurity Project of the Year, for a SOC monitoring project
- A SOC and SNOC that run 24×7
Simply Data Sdn Bhd, SSM registration 202201022568 (1468265-V), delivers its cybersecurity compliance services from Puchong, Selangor, with a 24×7 SOC.
We serve customers in Malaysia and Singapore, as well as across Southeast Asia. In Malaysia we hold NACSA licences. In Singapore we hold CSRO licences from the Cyber Security Agency of Singapore: CS/SOC/C-202609-1162 for managed SOC monitoring and CS/PTS/C-202609-1161 for penetration testing. You can see the full list on our certifications and awards page.
Last reviewed: 16 October 2026.
Further reading
Frequently Asked Questions
Simply Data provides technical PDPA compliance support in Malaysia, covering security controls, monitoring, testing and breach investigation. Your legal counsel and DPO handle legal interpretation of the Act, and we supply the technical work and reports they rely on.
For NCII entities, the Act and its 2024 regulations require a cyber security risk assessment at least once a year and a cyber security audit at least once every two years, or more often if directed by NACSA. Incidents must be notified immediately when known, with particulars within 6 hours and supplementary information within 14 days after the initial notification.
Simply Data can support the technical aspects of NCII compliance. We hold NACSA licences 20007-01 for Managed SOC Monitoring and 20007-02 for Penetration Testing under the Cyber Security Act 2024. We support NCII entities through Security Posture Assessment, compromise assessment, Managed SOC 24x7, cyber incident response, network configuration audit and hardening, and penetration testing.
Simply Data provides technical RMiT compliance support in Malaysia through Managed SOC 24x7, vulnerability assessment and penetration testing, and SIEM on Elastic (SD Unified Platform). RMiT specifies quarterly vulnerability assessments and annual intelligence-led penetration testing; confirm the required scope, schedule and log-retention capabilities for your environment. Your compliance team and auditors interpret RMiT and confirm which incident reporting deadlines apply.
Yes. Simply Data holds NACSA licence 20007-01 for Managed SOC Monitoring and 20007-02 for Penetration Testing under the Cyber Security Act 2024. In Singapore we hold CSRO licences CS/SOC/C-202609-1162 and CS/PTS/C-202609-1161.
No. Simply Data does not provide legal advice on PDPA or any other law. We deliver technical controls and evidence, and we work alongside your legal counsel, DPO and auditors. Legal interpretation stays with them, while the applicable notification duties remain with the data controller or NCII entity.
Want to map your PDPA, Cyber Security Act 2024 or RMiT obligations to technical controls and evidence? Contact Simply Data to talk to our team about cybersecurity compliance services for your environment and the evidence your auditors expect.
Get Your Free
Consultation Now!
We’re here to help! Whether you have questions about our Services!
- B-03A-03, 3RD Floor, Block B Setiawalk, Persiaran Wawasan, Pusat Bandar Puchong, 47160 Puchong, Selangor
- +603 5886 2714
- contactus@simplydata.com.my